For Europe’s aviation industry, cybersecurity is no longer just a background technical issue. It is now a regulatory obligation tied directly to operational continuity, passenger safety, and national resilience.
Airlines operate complex, interconnected digital environments.
From flight planning and maintenance coordination to passenger communications and ground operations, vast amounts of sensitive information move through digital channels every hour. And when those communications are disrupted, intercepted, or mishandled? The consequences go far beyond delayed flights.
This reality is exactly why the European Union introduced the Network and Information Security Directive version two, known as the NIS2 Directive.
MailSPEC SAS works closely with aviation operators and critical infrastructure organizations across Europe, including France, where aviation plays a central role in economic and national security.
As airlines such as Air France adapt to the NIS2 Directive, one conclusion is becoming clear: encrypted communication protocols are no longer optional. They are foundational to compliance and resilience.
The NIS2 Directive is the European Union’s updated cybersecurity framework designed to strengthen the resilience of essential and important entities. It significantly expands both the scope and the enforcement power of the original Network and Information Security Directive.
Under NIS2, the transport sector, including aviation, is explicitly classified as critical infrastructure.
This means airlines, airport operators, air traffic services, and aviation support providers are now subject to:
For aviation leaders, NIS2 compliance for aviation is not a future requirement. It is an active responsibility.
Aviation systems are deeply interconnected. A single disruption? Can cascade across borders, airports, and supply chains
Digital communications support:
Because these systems rely heavily on real-time digital communication, the NIS2 Directive places special emphasis on protecting how information moves, not just where it is stored.
This is where encrypted communication protocols become essential.
The NIS2 Directive requires organizations to adopt “appropriate and proportionate technical and organizational measures” to manage cybersecurity risks.
And for aviation, this includes digital communication systems.
Airlines must demonstrate that they:
Consumer-grade communication tools and generic cloud messaging platforms struggle to meet these expectations.
By contrast, encrypted communications designed for NIS2 compliance provide built-in safeguards aligned with regulatory intent.
Encryption ensures that information cannot be read or altered by unauthorized parties. But under NIS2, encryption must be implemented in a way that supports accountability and governance.
This means:
And for aviation operators, encrypted communication is not just about secrecy. It is about controlled transparency.
One of the most significant shifts under NIS2 is the emphasis on digital sovereignty.
European regulators increasingly expect critical infrastructure providers to understand:
For airlines operating across borders, this matters deeply.
If communication systems rely on foreign-owned infrastructure or opaque cloud services, airlines may face exposure to:
Sovereign control of data ensures that encrypted communications remain under European governance, supporting both compliance and trust.
NIS2 introduces strict timelines for reporting major information and communication technology incidents.
Aviation organizations must now:
Without secure, auditable communication systems, incident reporting becomes chaotic.
Encrypted communication platforms that automatically log access, preserve records, and support forensic review give aviation operators a critical advantage when responding under pressure.
Forward-looking airlines are already rethinking how their teams communicate.
Instead of relying on fragmented tools, they are moving toward secure messaging for aviation compliance that offers:
These systems allow teams to move quickly while remaining compliant.
Speed and security no longer have to compete.
Large carriers like Air France operate in one of the most regulated environments in the world. Their approach to cybersecurity often sets the tone for the industry.
As aviation leaders align with NIS2 requirements for airlines, encrypted communication protocols are becoming standard across:
This shift reflects a broader understanding: communication systems are part of the safety framework.
MailSPEC SAS operates with a strong presence in Paris and Nice, placing it close to Europe’s aviation, transport, and regulatory hubs.
This local presence matters.
It enables MailSPEC to:
MailSPEC’s secure communication solutions are designed for environments where compliance is not theoretical. It is operational.
One concern aviation leaders often raise is usability.
Will secure systems slow teams down?
In practice, modern encrypted communication platforms designed for regulated industries deliver:
The result is not friction, but confidence.
Teams communicate freely, knowing the system protects them.
Airlines preparing for NIS2 compliance should assess their communication infrastructure honestly.
Ask the following:
Now, if gaps exist, encrypted communication protocols should be prioritized.
NIS2 compliance is not just about avoiding penalties.
For aviation leaders, secure communication:
✔️ Protects passenger trust
✔️ Preserves operational continuity
✔️ Strengthens relationships with regulators
✔️ Reduces exposure to cascading digital failures
In a sector where reliability defines reputation, this matters.
The NIS2 Directive signals a new era of accountability for Europe’s aviation industry.
Airlines are no longer judged solely on physical safety or punctuality. They are judged on digital resilience.
And encrypted communication protocols sit at the heart of this shift.
With sovereign control, audit-ready design, and strong encryption, aviation leaders can meet NIS2 requirements while continuing to operate at scale.
MailSPEC SAS supports this transition by delivering secure, compliant communication solutions built for European critical infrastructure.
Because under NIS2, how you communicate is how you protect the skies.
For companies operating inside the defense industrial base, cybersecurity is no longer a competitive advantage. It is a contractual requirement.
Every message, email, file transfer, and internal chat that touches defense-related work now falls under closer scrutiny. The shift to the Cybersecurity Maturity Model Certification version 2.0 framework makes this clear: Communication systems are no longer peripheral tools. They are part of the security perimeter itself.
MailSPEC collaborates with defense contractors, aerospace manufacturers, and government suppliers as they navigate this transition. Across the industry, one pattern continues to emerge. Organizations invest heavily in firewalls, endpoint protection, and network security, but overlook how sensitive information actually moves day to day. It moves through messages.
Under Cybersecurity Maturity Model Certification version 2.0, secure messaging for all defense industrial base contractors is no longer optional. It is foundational.
The Cybersecurity Maturity Model Certification framework was created to protect sensitive defense information across the supply chain. Version 2.0 simplifies the structure but strengthens expectations.
And instead of multiple overlapping maturity levels, the updated framework focuses on clearer tiers aligned to real risk.
Level One focuses on basic cyber hygiene.
Level Two addresses the protection of Controlled Unclassified Information.
Level Three applies to organizations handling the most sensitive defense programs.
For most defense industrial base contractors, Level Two is the operational reality. And Level Two explicitly requires safeguards that prevent unauthorized access, disclosure, and transmission of Controlled Unclassified Information.
This is where CMMC 2.0 secure messaging becomes critical.
Controlled Unclassified Information does not only live in databases or engineering systems. It travels.
It is discussed in internal chats.It is referenced in emails.It is shared in attachments, meeting notes, and quick messages sent to “keep things moving.”
CMMC communication requirements focus on how information is protected in transit, not just at rest. A messaging system that lacks proper encryption, access control, and auditability becomes a direct compliance gap.
Here, secure messaging is not about convenience. It is about containment.
End-to-end encryption ensures that messages are protected from the moment they leave the sender until they are received by the intended party. No intermediary, administrator, or third party can read the contents.
For defense contractors, this matters because:
However, encryption alone is not enough.
If encryption keys are controlled by a third party, or if messages pass through public cloud infrastructure outside organizational control, the risk remains.
This is why secure messaging for CMMC 2.0 compliance must also include sovereign control.
Public cloud platforms were designed for scale and convenience, not defense-grade assurance.
Defense contractors face specific risks when relying on public cloud messaging systems:
And under Department of Defense expectations, these risks are unacceptable.
A compliant messaging system must allow the contractor to define where data lives, who administers it, and how it is accessed.
MailSPEC was designed for environments where sovereignty, jurisdiction, and control are non-negotiable.
Rather than forcing defense organizations into shared public infrastructure, MailSPEC enables:
✔️ Sovereign or on-premise deployment
✔️ End-to-end encryption across email, chat, file sharing, and video
✔️ Key Fusion consent is eDiscovery for decryption
✔️ Immutable journaling for secure recordkeeping
✔️ Role-based access controls aligned with clearance levels
✔️ On client AI Governance engine for Policy enforcement and classification
This approach directly supports secure communication for defense contractors operating under Cybersecurity Maturity Model Certification version 2.0.
The defense supply chain is only as secure as its weakest link.
Prime contractors increasingly require subcontractors to demonstrate compliance not only with network security standards, but also with communication controls.
A single unsecured message can expose:
This is why CMMC compliant messaging solutions must extend across internal teams and external partners.
MailSPEC enables defense organizations to create a secure collaboration fabric where sensitive information is shared deliberately, logged automatically, and governed consistently.
Defense contractors preparing for Cybersecurity Maturity Model Certification assessments should start with a simple but honest audit.
Ask the following questions:
If the answer to any of these questions is “no” or “not sure,” secure messaging must be addressed immediately.
One concern defense contractors often raise is productivity. Will secure messaging slow teams down?
In practice, the opposite is true.
When secure messaging is integrated into daily workflows:
Security becomes invisible, but effective.
Cybersecurity Maturity Model Certification version 2.0 is not just about passing audits. It reflects a broader reality.
Defense organizations are targets.
State-sponsored actors do not only attack networks. They exploit weak communication channels, compromised credentials, and informal habits.
Secure messaging closes one of the most commonly exploited gaps.
Thus, by adopting secure messaging that meets Department of Defense expectations, defense contractors improve resilience, trust, and long-term operational integrity.
Public cloud platforms are not inherently insecure, but they are not designed for sovereign defense communication.
Defense contractors that continue to rely on them for sensitive messaging accept risks they cannot fully control.
Organizations that move to private, sovereign communication systems are making a strategic decision. They are choosing certainty over convenience.
They are choosing control over assumption.
The Cybersecurity Maturity Model Certification version 2.0 framework has clarified what defense contractors must do to protect Controlled Unclassified Information.
Secure messaging is no longer a “nice to have.” It is an operational requirement.
MailSPEC provides defense industrial base contractors with secure, sovereign communication systems that align with Department of Defense expectations, support global compliance frameworks, and protect sensitive information without disrupting mission-critical work.
Now is the time to evaluate how your messages move. Because in modern defense environments, secure messaging is security.
It usually starts with good intentions...
A broker sends a quick message to a colleague to confirm a trade detail.A client asks a follow-up question through a familiar chat app.A deal team keeps momentum by using the fastest tool already on their phones.
But for financial institutions? Those small choices can trigger massive regulatory consequences.
MailSPEC works with broker-dealers, investment advisers, and regulated financial organizations that face growing pressure from regulators to rein in off-channel communications. Under United States securities law, informal messaging habits are no longer a grey area. They are a direct compliance risk.
At the center of this issue is SEC Rule 17a-4 messaging compliance, a recordkeeping requirement that fundamentally changes how financial firms must handle electronic communications.
And as enforcement actions and penalties continue to rise, one thing has become clear: consumer chat applications like WhatsApp are not a viable option. Financial institutions need a robust alternative to WhatsApp that is purpose-built for regulatory oversight.
SEC Rule 17a-4 establishes strict requirements for how broker-dealers must preserve records related to their business activities. These rules apply to electronic communications just as much as paper records.
At its core, the rule requires firms to:
This includes messages related to trading, client instructions, internal decision-making, and operational coordination.
For compliance teams, SEC 17a-4 compliant messaging is not about convenience. It is about defensibility. If a message cannot be produced during an audit or investigation, regulators treat it as if it never existed, or worse, as if it was deliberately hidden.
Consumer messaging applications were never designed for regulated financial environments. While they may offer encryption and ease of use, they still fail in the areas that matter most under securities law.
WhatsApp and similar applications do not provide firms with guaranteed, tamper-proof records under organizational control. Messages can be deleted, edited, or lost across devices.
Compliance officers cannot monitor, archive, or enforce policy across personal chat accounts. Meaning, there is no consistent way to ensure every relevant message is captured.
During examinations, firms must demonstrate that communications are complete, intact, and unaltered. Consumer chat logs do not meet the evidentiary standards required by regulators.
This is why regulators classify these tools as off-channel communications. Even when business is conducted casually, the legal expectation remains the same.
Recent enforcement actions have made one thing unmistakably clear. Regulators are no longer accepting excuses about convenience or legacy habits.
That said, major financial institutions have faced penalties totaling hundreds of millions of dollars for failing to properly capture and retain business communications conducted through unauthorized messaging platforms.
And these cases share a common theme:
So, for compliance leaders, this has shifted the conversation from “Should we act?” to “How fast can we replace these tools?”
Replacing WhatsApp in a financial institution is not about finding another chat app. It is about deploying a communication system designed around regulation, not retrofitted for it.
A true robust alternative to WhatsApp must support:
This is where sovereign messaging systems become essential.
A sovereign messaging system places the firm in full control of its communication environment. Unlike consumer platforms, the organization owns the infrastructure, the data, and the compliance controls.
All messages are captured automatically. No reliance on employee behavior or manual exports.
Messages are stored in a format that prevents alteration or deletion, supporting long-term retention and audit requirements.
Rules can be applied before a message is sent, preventing sensitive information from leaving approved channels.
Every message includes metadata showing who sent it, when it was sent, and under which policy it was governed.
This approach transforms messaging from a liability into a controlled, auditable business process.
MailSPEC’s Pulse chat platform was designed specifically to address these regulatory challenges.
Pulse delivers secure messaging for broker-dealers while preserving the familiar experience employees expect from modern chat applications.
Pulse supports compliance journaling aligned with SEC Rule 17a-4 requirements. Messages are captured automatically, indexed, and preserved for audit readiness.
Pulse mirrors the simplicity of popular messaging apps, reducing resistance and eliminating the temptation to revert to unauthorized tools.
Pulse can also be deployed within private or national environments, ensuring that data remains under organizational and jurisdictional control.
Compliance teams can apply group controls, retention policies, and monitoring rules without disrupting workflows.
By embedding compliance directly into the communication layer, Pulse helps firms meet financial messaging compliance under SEC requirements without slowing down business.
One of the most overlooked risks in financial institutions is the blending of personal and professional messaging.
When employees use personal chat apps for work:
A compliant messaging platform creates a clear boundary. Employees know where business communication belongs, and compliance teams gain confidence that records are complete.
This separation then protects both the firm and the individual.
Many financial institutions already prohibit the use of unauthorized messaging tools on paper. The challenge is enforcement.
Without a compliant alternative that employees actually want to use, policies fail in practice.
A secure compliant messaging platform succeeds because it aligns behavior with regulation. Employees are not forced to choose between speed and safety. They get both.
The regulatory environment is not becoming more forgiving. Expectations around recordkeeping, supervision, and audit readiness continue to rise.
Firms that delay action risk:
Those that act decisively gain control, clarity, and confidence.
If your organization operates under securities regulation, unauthorized messaging is no longer a manageable risk. It is an enforcement priority.
MailSPEC helps financial institutions replace off-channel communication with secure, compliant messaging built for regulatory governance.
Learn how Pulse can serve as a robust alternative to WhatsApp while meeting SEC Rule 17a-4 messaging compliance requirements. Take control of your internal communications before regulators force the issue.
For many organizations, cloud services promise speed, convenience, and lower costs. But for companies operating in highly regulated industries, those promises often come with unacceptable tradeoffs.
Banks, defense contractors, aviation authorities, healthcare providers, and government agencies face a very different reality. Their internal communications carry sensitive data, national security information, financial records, or legally protected personal details.
In these environments, sending messages through public cloud services like Gmail or Office 365 is not just risky.
And in many cases, it is explicitly forbidden.
This is where secure internal communications for regulated industries become a strategic necessity rather than a technical preference.
MailSPEC works with organizations across the Americas, Europe, and Japan that have made a deliberate decision to step away from public cloud platforms. These organizations are not trying to slow down their teams or reject modern tools. They are choosing control, accountability, and long-term compliance over convenience.
To understand why regulated organizations avoid public cloud services, it helps to look at both the legal and technical realities behind those platforms.
Public cloud communication tools are built for scale. They are designed to serve millions of users across borders, jurisdictions, and industries. And of course, that design works well for everyday collaboration, but it clashes directly with regulatory requirements in sensitive sectors.
Many regulations require organizations to know exactly where their data is stored, who can access it, and under which legal authority it falls. Public cloud services often store data in multiple locations, sometimes outside the country where the organization operates.
This creates problems such as:
For regulated industries, these risks are not theoretical. They carry real legal and financial consequences.
Even when cloud providers offer encryption, organizations rarely control that encryption end-to-end. The service provider typically manages key infrastructure, updates, and access mechanisms.
This also means companies must trust a third party not only with storage, but with the technical ability to access or influence communications.
For industries that require secure internal communications without using public cloud services, that trust model simply does not meet regulatory standards.
Unlike general-purpose messaging tools, secure internal communications in regulated environments are designed around control first, convenience second.
These systems prioritize:
Here, rather than asking, “How fast can we deploy this?” regulated organizations ask, “Can we defend this architecture in front of a regulator, a court, or a national authority?”
In the defense sector, internal communication systems handle classified information, operational plans, and sensitive personnel data. Even a minor exposure can have national consequences.
Defense organizations typically rely on non-cloud communication platforms that operate entirely within controlled environments. These platforms are often deployed on private infrastructure, isolated from the public internet, and governed by strict access controls.
In this context, public cloud services are excluded because:
For defense organizations, private communication systems for regulated industries are not optional. They are a baseline requirement.
Financial institutions operate under some of the strictest communication rules in the world. Regulators expect firms to retain records, monitor communications, and prove compliance long after messages are sent.
And public cloud messaging tools struggle to meet these expectations consistently.
Financial institutions require:
This is why many banks and trading firms deploy secure enterprise messaging without cloud dependency. These systems allow compliance teams to enforce rules at the moment communication happens, not after a problem occurs.
In aviation, communication errors can have immediate safety implications.
Maintenance teams, operations staff, and flight coordination groups rely on fast, accurate information exchange.
And at the same time, aviation authorities must also protect sensitive infrastructure data and passenger information.
Public cloud platforms introduce uncertainty around data handling and access control.
As a result, aviation organizations often deploy on-premise communication solutions that operate within tightly managed networks. These systems ensure that communication remains available, secure, and compliant even during outages or geopolitical disruptions.
Running secure internal communications without using public cloud services requires a different approach to infrastructure.
Key components include:
Organizations deploy communication systems within their own data centers or within trusted national environments. This ensures data remains under local legal authority.
Messages are encrypted end to end, with encryption keys controlled by the organization, not a third-party provider.
Compliance rules are enforced automatically during message creation and delivery. This prevents accidental data exposure before it happens.
All communications are recorded in tamper-proof archives that support audits, investigations, and regulatory reviews.
Only authorized users can access specific communication channels, based on role and responsibility.
Together, these components form the backbone of compliant internal communication tools.
MailSPEC was designed specifically for organizations that operate in complex regulatory environments.
Plus, rather than offering a single product, MailSPEC provides a unified platform that supports secure communication across multiple channels while maintaining sovereign control.
EasyCrypt provides encrypted email communication while allowing organizations to maintain full control over infrastructure and encryption policies. CommuniGate SPEC then serves as a sovereign email server for organizations that require complete ownership of their messaging environment.
Pulse enables real-time internal messaging without relying on public cloud services.
Conversations remain encrypted, auditable, and governed by organizational policy.
PassLink allows teams to exchange sensitive documents securely, with full visibility into access and usage. Files never leave controlled infrastructure.
JACE acts as the compliance engine behind all MailSPEC tools. It automatically journals communications, applies metadata, and supports secure escrow for audits and legal discovery.
By combining these capabilities, MailSPEC supports secure internal communications for regulated industries across the Americas, Europe, and Japan.
Choosing not to use public cloud services is not a step backward. For many of the world’s most secure brands, it is a strategic decision that reflects maturity and foresight.
Avoiding public cloud platforms allows organizations to:
In a world where data regulations continue to tighten, control becomes a competitive advantage.
As regulations evolve and geopolitical tensions increase, organizations will face growing pressure to demonstrate ownership and accountability over their communications.
Those that rely entirely on public cloud platforms may find themselves scrambling to retrofit compliance into systems that were never designed for it.
Organizations that invest early in secure internal communications without using public cloud services are better positioned to adapt, comply, and grow with confidence.
If your organization operates in a regulated industry, now is the time to reassess whether your communication tools truly meet your legal and security obligations.
MailSPEC helps regulated organizations replace public cloud dependence with a secure, sovereign, and compliant communication infrastructure.
To learn how your organization can strengthen governance in communications without compromising speed or usability, connect with MailSPEC.
Start building a communication environment you fully control.
For many organizations operating in Japan, secure communication is no longer just a technical discussion. It is now a matter of corporate responsibility, national compliance, and long-term trust.
Every internal message, shared document, or executive conversation carries more than information. It carries personal data, business intelligence, and in many cases, legally protected records.
Also, as Japan continues to strengthen its regulatory expectations around data protection and digital sovereignty, companies are being forced to re-examine a basic assumption they once took for granted: Who actually controls their messages once they are sent?
Now this question sits at the heart of sovereign-based messaging.
MailSPEC works with Japanese enterprises and public service organizations that are navigating this exact challenge. And these organizations are not simply looking for stronger encryption. They are looking for certainty.
Certainty about where their data lives. Certainty about who holds the keys. Certainty that their most sensitive communications remain fully under Japanese legal authority.
And that is why sovereign messaging in Japan is rapidly becoming the preferred model for security-conscious firms.
Before diving into regulations and risk, it helps to clearly define what “sovereign-based messaging” actually means.
At its simplest, sovereign-based messaging is a communication model where:
In other words, the company sending the message does not hand control to an external platform once communication begins.
This is very different from traditional cloud messaging services, where data may be encrypted but still processed, stored, or managed by providers operating under foreign legal frameworks.
And for Japanese businesses, that distinction matters deeply.
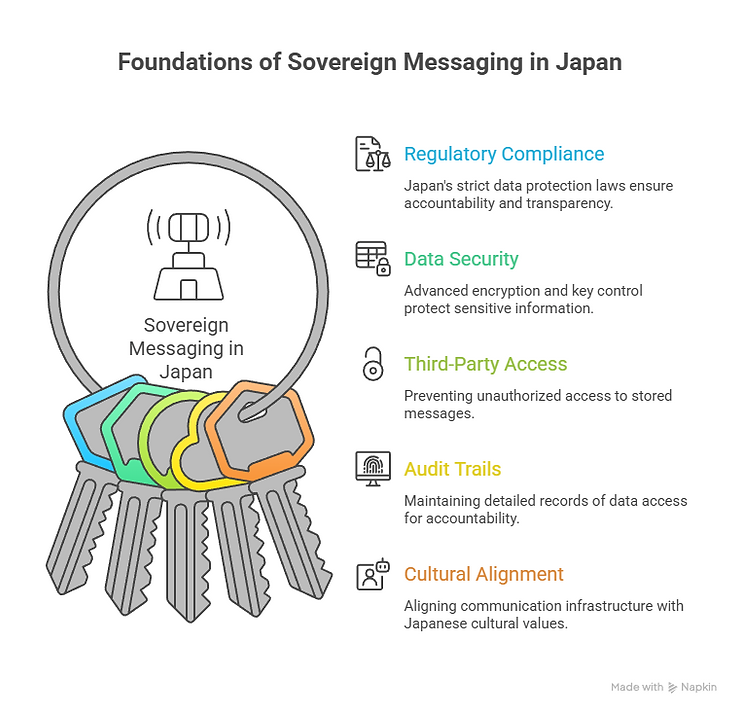
Japan’s regulatory environment places a strong emphasis on accountability, transparency, and protection of personal information. Under the Act on the Protection of Personal Information, organizations are expected to maintain strict oversight over how personal data is handled, stored, and shared.
This expectation extends beyond just basic encryption.
Japanese regulators and compliance teams increasingly look at:
This is why data sovereignty messaging in Japan is no longer a niche requirement. It is becoming a baseline expectation for regulated industries, large enterprises, and public-facing organizations.
Sovereign-based messaging allows Japanese firms to align their communication infrastructure with both legal requirements and cultural expectations around trust and responsibility.
Many companies believe they are protected simply because their messaging tools advertise “strong encryption.”
But encryption alone does not equal control.
In many popular messaging platforms, encryption is implemented inside what can only be described as a black box.
Messages may be encrypted, but the platform provider:
From a technical standpoint, this means the organization does not have absolute authority over its own communications.
From a regulatory standpoint? This creates exposure.
Japanese compliance leaders increasingly recognize that secure sovereign messaging requires more than trusting a vendor’s promise. It requires architectural ownership.
Trust plays a central role in Japanese business relationships.
Customers trust companies to protect their information. Partners trust organizations to handle shared data responsibly. Employees trust leadership to safeguard internal communication.
So, when data control is outsourced to foreign platforms, that trust becomes fragile.
Japanese organizations place high value on:
Sovereign communication platforms align naturally with these values. They ensure that responsibility for data protection remains where it belongs: with the organization itself.
This cultural alignment is one reason secure messaging for Japanese enterprises is increasingly built around sovereign principles rather than convenience-driven cloud services.
The Act on the Protection of Personal Information requires organizations to implement appropriate safeguards to prevent unauthorized access, leakage, or misuse of personal data.
In practice, this means companies must be able to demonstrate:
Sovereign-based messaging Japan solutions make these requirements easier to meet by design. Here, instead of layering compliance controls on top of a generic platform, sovereign systems embed compliance into the communication flow itself.
MailSPEC was built specifically to address the challenges that arise when security, compliance, and sovereignty intersect.
For Japanese enterprises, MailSPEC provides sovereign communication platforms that ensure:
✔️ Data remains within Japan
✔️ Encryption keys are controlled by the organization
✔️ Communication is protected end-to-end
✔️ Compliance policies are enforced automatically
MailSPEC’s architecture is designed to support organizations that cannot afford ambiguity around data ownership.
Rather than relying on one single tool, MailSPEC delivers sovereign control across multiple communication channels.
Pulse provides encrypted, real-time messaging designed for internal teams and regulated environments. Conversations remain fully under organizational control, with access governed by role-based policies and audit-ready logs.
This allows Japanese enterprises to replace consumer chat tools without sacrificing speed or usability.
EasyCrypt ensures that email communication remains encrypted both in transit and at rest, while keeping encryption control within Japan. Messages never become exposed to foreign cloud systems, even when communicating externally.
PassLink allows organizations to share sensitive documents through encrypted links with verified access. Files remain stored within sovereign infrastructure, with full visibility into who accessed them and when.
JACE acts as the policy and compliance backbone across all MailSPEC tools. It automatically journals communications, tags data for retention, and provides escrow capabilities for audits and legal requests.
Together, these tools create a unified sovereign messaging environment rather than isolated security features.
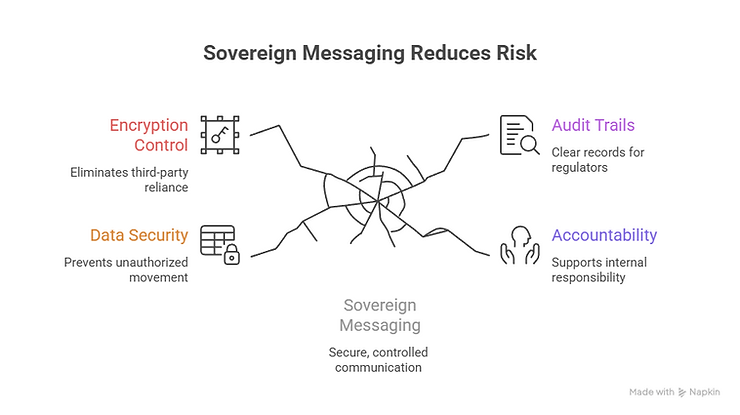
Security incidents are rarely caused by malicious intent. More often, they happen because systems were not designed for the realities of modern communication.
Sovereign-based messaging reduces risk by:
For Japanese firms operating in global markets, this approach offers stability in an increasingly complex regulatory landscape.
When evaluating sovereign-based messaging Japan solutions, organizations should ask:
MailSPEC addresses these questions directly, without forcing organizations to compromise usability for security.
As regulatory expectations continue to rise and global data flows become more scrutinized, sovereign control will only grow in importance.
Japanese enterprises that adopt sovereign-based messaging today are not just solving current compliance needs. They are also future-proofing their communication infrastructure against evolving regulations and emerging risks.
Sovereignty is no longer a theoretical concept. It is a practical requirement.
If your organization operates in Japan or handles Japanese personal data, now is the time to evaluate whether your messaging systems truly reflect your security and compliance obligations.
MailSPEC helps Japanese enterprises move beyond surface-level encryption and toward genuine sovereign control.
To learn how sovereign-based messaging can strengthen your security posture while supporting APPI compliance, connect with MailSPEC today.
Start building a communication environment you fully own and control.
It does not begin with a cyberattack. It begins with a decision.
A decision about where data lives.
Who owns the servers?
Who controls the encryption keys?
And who ultimately has the power to access systems that keep entire countries running?
Across Europe, organizations responsible for energy, transport, water, and public utilities are rethinking how their most sensitive data is stored and protected. Not because technology has failed them, but because control has quietly slipped out of their hands.
MailSPEC collaborates directly with European organizations operating under strict data protection and infrastructure security requirements. And what we see again and again is this: once leaders fully understand what sovereign control of data actually means, public and foreign-owned cloud services are no longer acceptable for critical infrastructure.
And this article explains why.
Sovereign control of data is often misunderstood as a legal concept. In reality, it is a technical and operational one.
At its core, sovereign control of data means full ownership and authority over three things:
So, if any one of these elements is controlled by an external party, true data sovereignty does not exist.
And for critical infrastructure in Europe, this distinction matters deeply.
These systems are not just business platforms. They manage power grids, rail networks, water treatment facilities, and emergency services. A single unauthorized access event can ripple outward into real-world harm.
This is why data sovereignty for critical infrastructure in Europe has moved from policy discussions into board-level decision-making.
For many years, public cloud platforms promised flexibility, scale, and cost savings. For standard office workloads, that promise often holds true.
But for critical infrastructure, the risk profile is completely different.
European energy, transport, and water companies are increasingly stepping away from foreign-owned cloud providers for several reasons:
When servers or encryption systems are owned by non-European entities, they may fall under foreign legal authority. This can allow external governments to compel access to data, even when that data belongs to European citizens or infrastructure.
And from a sovereignty perspective? This is clearly unacceptable.
Public clouds operate on shared physical systems. Even with strong logical separation, the underlying infrastructure is not exclusive. This creates exposure paths that critical infrastructure operators cannot fully control.
Many cloud providers manage encryption on behalf of customers. Say, if the provider controls the keys, the provider controls access. Sovereign control of data requires that encryption keys be owned and managed by the organization itself.
Which is why sovereign data control in Europe is now viewed as a national resilience issue, not just an information technology preference.
Critical infrastructure depends on trust.
Not abstract trust, but operational trust that systems will behave exactly as expected under stress.
When data is sovereign:
This level of control prevents external interference, whether accidental or intentional.
For example:
Now, if any of these systems were accessed or altered by an external entity, the consequences would extend far beyond compliance penalties. Thus, critical infrastructure data security in Europe increasingly depends on sovereign hosting models.
Regulations such as the General Data Protection Regulation are often cited as the reason organizations change their data strategies. But compliance alone is not enough.
The regulation emphasizes:
However, compliance does not automatically guarantee sovereignty.
A system can technically meet regulatory requirements while still relying on infrastructure owned and operated by foreign entities.
European regulators are increasingly aware of this gap. As a result, secure data hosting in Europe is now evaluated not just on encryption standards, but also on ownership, governance, and operational independence.
Sovereign control is not about isolation. It is about clear boundaries.
When infrastructure is sovereign:
This prevents:
In practical terms, sovereign cloud for critical infrastructure means that only the infrastructure owner can decide who sees what, when, and why.
MailSPEC provides secure communication environments specifically designed for regulated and high-risk sectors.
Rather than adapting consumer platforms for compliance, MailSPEC builds systems where sovereign control is foundational, not optional.
European organizations use MailSPEC to ensure:
✔️ Data remains hosted in sovereign environments
✔️ Encryption keys are controlled locally
✔️ Communication systems align with European regulatory and infrastructure standards
This approach then supports both European data sovereignty and operational continuity.
One of the most common misconceptions about data security is that encryption alone is sufficient.
Encryption only protects data when the right party controls the keys.
When encryption keys are generated, stored, or managed by an external service provider, true ownership is compromised. Sovereign systems ensure that:
This guarantees that even if data is intercepted, it remains unreadable to anyone outside the organization.
Critical infrastructure does not operate on documents alone. It relies on constant communication.
MailSPEC enables sovereign messaging through tools designed for environments where failure is not an option.
EasyCrypt ensures that email communications containing sensitive operational or personal data are encrypted at all times. Data is removed from foreign cloud environments and stored within sovereign infrastructure.
Pulse provides secure real-time messaging with immutable logs and role-based access controls. It allows teams to communicate quickly without exposing infrastructure data to consumer platforms.
PassLink enables secure file exchange using sovereign storage and verified access, ensuring that schematics, reports, and operational files are shared safely.
JACE ensures that all communication is logged, indexed, and auditable while remaining under sovereign control. This supports both regulatory requirements and operational accountability.
Together, these tools form a communication ecosystem where sovereign control of data is enforced by design.
Moving to sovereign systems is not just a technical migration. It is a strategic commitment to resilience, independence, and long-term security.
Organizations that make this shift gain:
And for critical infrastructure in Europe, this approach is becoming the standard rather than the exception.
In a connected world, complete isolation is impossible. But uncontrolled dependency is avoidable.
Sovereign control of data gives European critical infrastructure operators something invaluable: certainty.
Certainty about who owns the systems. Certainty about who can access them. Certainty that essential services remain protected, even under pressure.
MailSPEC then helps European organizations build this certainty into their communication and data environments from the ground up.
If your organization supports energy, transport, water, or other essential services, sovereign control of data is no longer optional.
Learn how secure, sovereign communication environments can protect your infrastructure, your data, and the people who rely on them every day.
It usually starts innocently.
A quick message to a colleague. A fast update to a group chat. A document was shared “just this once” to keep work moving.
For many enterprise teams across North America, Central America, and South America, consumer chat apps feel like the fastest way to get things done.
Familiar, simple, and already installed on everyone’s phone.
But behind that convenience sits a growing problem…
As regulations tighten and data moves faster than ever, unsafe chat apps are quietly becoming one of the biggest risks inside modern organizations.
MailSPEC collaborates with regulated enterprise teams across the Americas and sees this exposure surface again and again, often only after compliance or security teams raise the alarm.
That is why companies are now turning to secure messaging for enterprise teams as a replacement, not just an add-on.
And this shift is not about slowing people down. It is about protecting the business while keeping communication just as fast.
Let us be honest. People do not choose consumer messaging apps because they want to break the rules.
They choose them because they work.
These apps are:
And when an employee needs a quick answer, they are not actually thinking about data protection laws or audit trails. They are thinking, “How do I get this done right now?”
This behavior is especially common in:
So, from the employee’s perspective, it feels harmless. But from the organization’s perspective? It creates a serious risk.
Consumer chat applications are designed for social interaction, not enterprise accountability. And even when they advertise encryption? There are still gaps that matter deeply to regulated businesses.
Most consumer apps do not allow organizations to:
Once a message is sent, the organization often loses visibility and authority.
In regulated industries, the ability to prove what happened is just as important as preventing breaches.
Unsafe chat apps typically lack:
This makes compliance nearly impossible when regulators ask questions.
Many consumer platforms store data across global infrastructure without clear regional boundaries.
So, for enterprise teams operating across the Americas, this can violate local data protection laws or contractual obligations.
When business communication lives inside personal chat apps, it also lives on personal devices.
That means:
And these risks are not just theoretical. They are already driving regulatory penalties and legal disputes.
A dedicated enterprise messaging system is built with a different goal.
It is not trying to connect friends.It is trying to protect organizations.
Secure messaging for enterprise teams delivers the same instant experience people expect, while adding the safeguards businesses require.
The best platforms feel just as fast as consumer apps, but behave very differently behind the scenes.
One of the biggest fears leaders have is adoption.
They ask:“If we take away consumer chat apps, will people actually use the replacement?”
Well, modern secure team communication platforms are designed to answer that concern directly.
They offer:
From the user’s perspective, the experience feels familiar.
From the organization’s perspective, everything is controlled, logged, and protected.
Large organizations in the Americas face unique challenges.
Teams are often distributed across:
This makes secure business messaging in the Americas more complex than a single-country deployment.
An enterprise messaging system must:
And this is where consumer apps fall apart, and enterprise-grade platforms excel.
MailSPEC’s Pulse platform was designed specifically to replace unsafe chat apps in regulated environments.
Pulse provides real-time chat and collaboration, but with enterprise-grade control built in from the start.
Key capabilities include:
✔️ Encrypted messaging that protects content in transit and at rest
✔️ Centralized administrative control over users and groups
✔️ Non-rewritable, non-erasable message records
✔️ Policy enforcement that works automatically
So, instead of trusting users to “do the right thing,” Pulse enforces the rules for them.
Many consumer platforms claim to be encrypted. But that does not mean they are suitable for enterprise use.
Encryption answers one question: “Can outsiders read the message?”
Enterprise chat security must answer many more:
Pulse addresses these questions through integration with the JACE Compliance System, which provides journaling, archival, and policy enforcement across all communication.
If an organization is serious about replacing unsafe chat apps, the new platform must do more than look good.
Here is a practical checklist of must-have features for secure messaging for enterprise teams:
1. End-to-End Encryption with Enterprise Control
Messages MUST be encrypted, but encryption keys and policies MUST also be controlled by the organization.
2. Centralized Administration
Security and compliance teams need both visibility and authority across all users and conversations.
3. Immutable Message Logs
Messages should not be alterable or erasable in ways that undermine audits or investigations.
4. Role-Based Access
Not every user should see every conversation. Access must follow job function and policy.
5. Data Residency Options
Data should stay where regulations and business requirements demand.
6. Seamless User Experience
Is the tool hard to use? Employees will find workarounds.
7. Integration with File Sharing
Chat often includes documents. File exchange must be just as secure as messages.
Note: Pulse, combined with PassLink for file sharing, was built to meet these exact needs.
One of the biggest myths about secure messaging is that it slows teams down.
In reality, the opposite is often true.
When employees have a clear, approved platform:
Security becomes invisible, not obstructive.
This is also the philosophy behind MailSPEC’s broader Réunion Suite, where encryption, authentication, and compliance are part of the system, not extra steps.
Regulators across the Americas are paying closer attention to how organizations communicate.
Fines, investigations, and reputational damage increasingly trace back to informal, unsecured messaging. And at the same time, remote and hybrid work has made chat central to daily operations.
Hence, the result is clear: Unsafe chat apps are no longer a minor issue. They are a material risk.
Replacing consumer chat apps is not just a technical upgrade. It is a cultural shift.
Organizations that succeed do three things:
Secure messaging becomes the default, not the exception.
Speed and security do not have to compete.
With the right platform, enterprise teams across the Americas can communicate instantly, collaborate freely, and remain fully compliant.
Secure messaging for enterprise teams is no longer a luxury. It is a necessity for organizations that value trust, resilience, and long-term stability.
If your organization is ready to replace unsafe chat apps with a secure, enterprise-grade solution, MailSPEC can help.
Contact MailSPEC today. See how secure messaging can protect your business without slowing it down.
For most Chief Information Security Officers, regulatory risk does not come from a lack of rules. It comes from the gap between policy and reality.
Policies say sensitive information should never be shared in open chats. Reality says employees move fast, copy text, attach files, and make decisions in real time. Multiply that behavior across thousands of employees, dozens of countries, and overlapping regulatory frameworks, and even well-run organizations begin to feel exposed.
MailSPEC works closely with regulated organizations throughout North America, Central America, and South America that face this challenge at scale. And this is why more security leaders are also turning to AI Enabled Communication Tools as a practical way to manage regulatory risk without slowing the business down.
Note that these enterprises are not struggling because they lack policies or awareness. In fact, most already have strong governance frameworks in place. The real challenge here is volume, velocity, and human error.
Modern communication moves faster than traditional compliance controls were ever designed to handle.
Traditional compliance models were built for slower systems.
Email archives were reviewed weeks later. Chat logs were sampled. Violations were discovered after the message had already been sent, copied, and stored in multiple locations.
And for today’s CISO, that model creates three serious problems:
No amount of training fully solves this. People still make mistakes when they are under pressure.
This is where AI communication tools for regulatory compliance change the equation.
There is a lot of noise around artificial intelligence. For security leaders, the value is much more specific and much more practical.
In secure communication environments, artificial intelligence is used to:
In other words, these tools intervene before risk leaves the device, not after regulators start asking questions. This approach then turns compliance from a reactive process into a preventative one.
One of the most valuable shifts for CISOs is moving compliance enforcement to the point of communication.
Instead of asking, “What went wrong last quarter?” artificial intelligence allows teams to ask, “Should this message go out at all?”
AI tools for compliance management can detect:
And if a message violates policy, the system can:
This happens silently, in real time, without adding steps for the employee.
Many organizations try to bolt compliance tools onto existing communication systems. That approach almost always fails.
Why? Because risk happens inside the conversation, not after it.
And when artificial intelligence is integrated directly into the messaging platform, it can:
✔️ Observe context, not just content
✔️ Understand who is sending and who is receiving
✔️ Apply role-based rules automatically
✔️ Maintain data sovereignty
Now, this is what separates true AI-powered compliance monitoring from surface-level scanning tools. And MailSPEC’s compliance architecture was built around this principle.
At the center of MailSPEC’s compliance capabilities is the JACE Compliance System, an artificial intelligence-driven policy engine designed for regulated communications.
JACE does not operate in the cloud. It sits directly on the communication channel, enforcing rules even before data leaves the user’s device. This preserves sovereign control and reduces exposure across borders.
JACE enables:
For CISOs, this means compliance enforcement without user disruption.
Organizations in the Americas often face overlapping regulatory obligations.
A single company may need to comply with:
Thus, manual enforcement across these frameworks is nearly impossible.
AI communication security for enterprises provides consistency across geography, language, and business units. Policies are applied centrally, but enforced locally, inside every message.
This is how large organizations maintain control without slowing global operations.
Most compliance failures are not malicious. They are accidental.
An employee copies information from one system into a chat. A file is sent to the wrong group. A conversation moves faster than policy review.
Artificial intelligence addresses this reality by acting as a silent guardrail.
Instead of blaming users after the fact, AI Enabled Communication Tools guide behavior in the moment. The system becomes an invisible compliance officer always present, never obstructive. This then dramatically reduces incident rates while improving employee trust.
For CISOs, secure messaging is no longer just an operational tool. It is a strategic control layer.
MailSPEC’s secure communication environment combines:
Together, these tools form a unified platform where artificial intelligence enforces regulatory intent automatically.
What modern CISO regulatory risk management tools look like in practice.
Beyond risk reduction, artificial intelligence saves time in areas that matter to executive leadership.
With automated compliance:
Instead of scrambling during regulatory inquiries, CISOs can present structured, searchable records with confidence.
This shifts compliance from a cost center to a source of operational stability.
Across regulated industries, security leaders are reaching the same conclusion.
Training alone is not enough. Policy documents do not enforce themselves. Manual review does not scale.
AI Enabled Communication Tools provide:
✔️ Continuous oversight
✔️ Immediate enforcement
✔️ Reduced human error
✔️ Stronger audit readiness
For organizations navigating complex regulatory environments in the Americas, this approach is no longer optional.
Regulatory pressure is not going away. Communication volume is only increasing.
The only sustainable path forward is compliance that works at the speed of human decision-making.
By embedding artificial intelligence directly into secure communication systems, organizations can protect sensitive information, reduce risk, and support business velocity at the same time.
MailSPEC helps CISOs achieve this balance with secure, sovereign, AI-driven communication platforms designed for regulated environments.
So, if your organization is ready to move from reactive compliance to intelligent prevention, it is time to explore AI Enabled Communication Tools built for regulatory reality.
Learn how artificial intelligence can strengthen your compliance posture without slowing your teams down.
There is a quiet shift happening inside boardrooms, security operations centers, and compliance teams at some of the world’s largest organizations.
It usually starts with a simple question from a Chief Information Security Officer or a Chief Compliance Officer:
“Are we actually in control of our most sensitive communications?”
For years, platforms like Office 365 have been the default answer for enterprise productivity. Email, documents, chat, video calls, everything in one place, delivered through a massive public cloud. For general business use, this convenience makes sense.
But when communications fall under strict regulatory oversight? Convenience can quickly turn into risk.
That is why global brands are actively searching for Office 365 alternatives for regulated communications, and why regulated industries are rethinking what “secure enough” really means.
And MailSPEC provides this alternative.
Public cloud platforms are built for scale. Millions of users. Thousands of features. Continuous updates.
But that strength is also their biggest weakness for regulated communications.
A one-size-fits-all service must balance ease of use, global availability, and commercial flexibility. It cannot be built around the specific legal, privacy, and sovereignty requirements of every regulated industry in every country.
For organizations operating under strict rules, this creates uncomfortable trade-offs:
And when regulators ask hard questions, vague assurances are no longer enough.
Not all communication is created equal.
A casual internal message about a meeting time is very different from:
These are regulated communications, and they carry legal obligations that general office software was never designed to fully satisfy.
Highly regulated organizations require tools that are:
Now, this is where regulated communication software begins to diverge sharply from general-purpose platforms like Office 365.
Imagine the role of a Chief Information Security Officer at a multinational company.
Operations span North America, Europe, and Asia. Each region has its own data protection laws, retention rules, and regulatory expectations.
Now picture this moment:
A regulator asks for proof that sensitive communications were encrypted, retained correctly, and never accessed outside approved jurisdictions.
The CISO opens dashboards. Exports reports. Reviews third-party documentation. Coordinates with cloud providers. And still feels uneasy.
Why?
Because in a public cloud model, ultimate control does not belong to the organization. And this is the pain point driving the search for secure alternatives to Office 365.
Public cloud providers do offer security features. Encryption, logging, retention policies. All exist on paper.
Now, the issue here is ownership and control.
With public cloud platforms:
For regulated organizations, this creates dependency rather than sovereignty.
And when regulations require absolute certainty, “trust us” is not a sufficient control model.
This is where the comparison becomes clear.
Sovereign systems are not about rejecting the cloud entirely. They are about choosing who controls it.
Across finance, healthcare, government, and critical infrastructure, organizations are making the same calculation.
Note that they are not abandoning Office 365 for everyday productivity. They are simply separating routine work from highly regulated communications.
This separation allows them to:
Again, this is a strategic decision, not a technical one.
The trend is clear.
Large organizations are adopting compliant communication platforms that run alongside general office tools.
These platforms focus on:
Here, you are not just adding another tool. You are building a compliance foundation that regulators can trust.
MailSPEC was built on a simple idea: regulated communications deserve their own infrastructure. So, instead of adapting consumer-grade tools, MailSPEC designs systems to regulation specifications from the ground up.
MailSPEC solutions are aligned with major regulatory frameworks, including healthcare privacy, financial oversight, data protection laws, and national information standards.
This includes:
✔️ End-to-end encrypted email, chat, and file sharing
✔️ Immutable journaling and archival
✔️ Policy enforcement that happens automatically
✔️ Jurisdictional sovereignty and data residency
And this is why MailSPEC is considered among the most trusted enterprise messaging compliance solutions.
One of the biggest frustrations with public cloud platforms is complexity. Compliance teams do not need more dashboards. They need clarity.
MailSPEC platforms provide:
So, instead of reacting to compliance issues after the fact, teams gain control at the point of communication.
Several forces are pushing organizations away from one-size-fits-all platforms:
In this environment, regulated communications are no longer a secondary concern.
They are a strategic priority.
Convenience built the modern workplace. Compliance will define its future.
As regulations tighten and scrutiny increases, organizations must ask harder questions about their communication infrastructure.
Global brands are answering those questions by moving toward Office 365 alternatives for regulated communications, platforms that prioritize control, security, and regulatory confidence.
MailSPEC exists for organizations that cannot afford uncertainty.
If your organization handles sensitive, regulated communications and needs greater control than public cloud platforms can offer, it may be time to rethink your approach.
MailSPEC provides sovereign, encrypted communication systems designed for the world’s most demanding regulatory environments.
Learn how private, compliant communication platforms can support your organization’s most critical work, without compromise.
It starts with a single test result.
A blood sample is taken at a diagnostic laboratory early in the morning. Then by midday, the analysis is complete. The results contain sensitive details about a patient’s health, information that must reach the right doctor quickly, accurately, and securely.
This moment, repeated thousands of times every day across Europe, is where modern healthcare either works smoothly or quietly fails.
And for years, care providers relied on email, fax machines, and even phone calls to move this information from one place to another. But as healthcare systems become more digital, more connected, and more regulated, those older methods are no longer enough.
Today, professional care providers across Europe are moving to encrypted internal messaging for care providers in Europe, like MailSPEC, because patient safety, legal responsibility, and operational speed now depend on it.
Imagine the journey of that lab result.
The laboratory uploads the report. A nurse reviews it. A primary doctor needs to see it immediately. A specialist may need to be consulted, too.
All of this happens under time pressure and under strict data protection rules.
Now, if the report is sent through an unsecured channel, even accidentally, it creates risk:
And in a modern care environment, this is no longer acceptable.
Encrypted internal messaging allows that lab result to move securely through each step of the care process, visible only to authorized professionals, with every access recorded and protected.
Healthcare providers in Europe carry a legal and ethical duty to protect patient information at all times.
Under the General Data Protection Regulation, health data is classified as highly sensitive personal information.
This means providers MUST:
Failing to meet these obligations can result in serious consequences, including fines, reputational damage, and loss of patient trust.
This is also why GDPR compliant internal messaging is no longer optional. It is a foundational requirement for modern care organizations.
Many care providers still rely on a mix of legacy tools:
And while familiar, these tools introduce hidden risks.
Emails can be forwarded accidentally. Consumer chat applications are not designed for healthcare compliance. Paper records can be misplaced. Phone calls leave no traceable record.
Bottom line is, none of these methods provides the combination of speed, security, and accountability required in modern care delivery.
Encrypted internal messaging changes how healthcare teams communicate.
Instead of sending files through unsecured channels, staff communicate inside a protected environment designed specifically for sensitive data.
With encrypted healthcare messaging in Europe, care providers gain:
✔️ End-to-end encryption that protects data in transit and at rest
✔️ Role-based access so only the right people can see the information
✔️ Full audit trails for accountability
✔️ Faster collaboration without compromising safety
This approach supports both patient care and regulatory compliance.
One of the biggest misconceptions about secure communication is that it slows people down.
In reality? Encrypted internal messaging often improves efficiency.
Doctors no longer wait for emails. Nurses do not chase paper files. Specialists can review results instantly within a secure chat environment.
Thus, secure messaging for care providers is replacing older, slower communication methods. It allows care teams to act quickly while staying within legal boundaries.
Many data breaches in healthcare are not caused by hackers. They are actually caused by simple human error.
A message was sent to the wrong recipient. A file was attached to the wrong email. A chat forwarded outside the organization.
Encrypted internal messaging prevents these mistakes by design.
Features such as:
help ensure patient data stays where it belongs.
A critical reason care organizations are adopting private messaging for healthcare teams instead of consumer tools.
MailSPEC provides a secure communication infrastructure designed for regulated environments, including healthcare across Europe.
And rather than offering a generic messaging application, MailSPEC delivers purpose-built tools that support compliance, visibility, and patient safety.
Pulse provides real-time internal messaging with encryption and policy controls built in.
Healthcare teams can communicate instantly while maintaining:
Pulse delivers the speed clinicians expect, without the risks of consumer chat tools.
When lab reports, imaging files, or discharge documents must be shared, PassLink ensures they move securely.
With encrypted file transfer, verified access, and expiration controls, PassLink supports secure communication for care organizations without exposing patient data.
Some communication still relies on email. EasyCrypt ensures those messages remain protected.
Sensitive content is encrypted automatically, helping providers maintain compliance while continuing to use familiar workflows.
JACE provides the compliance backbone.
Every message, file, and interaction is securely logged, indexed, and available for regulatory review. This gives organizations confidence that they can demonstrate compliance at any time.
Encrypted internal messaging does more than protect data. It protects people.
Doctors gain confidence that their communication is secure. Administrators gain assurance that policies are being followed. Patients gain trust that their private information is respected.
This peace of mind is one of the most powerful reasons care providers across Europe are moving to encrypted internal messaging for care providers in Europe.
Healthcare is becoming more connected, more data-driven, and more regulated.
Thus, secure communication is no longer a technical upgrade. It is a core part of patient safety and professional responsibility.
Encrypted internal messaging allows care teams to work faster, collaborate better, and meet legal obligations without friction.
Every lab result tells a story. That story deserves protection from start to finish.
By adopting encrypted internal messaging, care providers across Europe are building systems that support both excellent care and strict compliance.
MailSPEC helps healthcare organizations make that transition with secure, compliant communication tools designed for regulated environments.
So, if your organization is ready to modernize internal communication while protecting patient trust, now is the time to explore encrypted internal messaging built for healthcare.
Learn how secure communication can support safer, faster, and fully compliant care delivery.
Subject related to Cybersecurity, whether that be MailSPEC products and services, or the industry.
When it comes to mergers and acquisitions (M&A), the stakes are high—and so are the risks. From all your financial projections and legal documents to those personnel decisions and proprietary data, the information shared during these deals is some of the most sensitive information an organization like yours can hold.
Yet, despite the critical nature of this process, many still rely on unsecured or inconsistent communication methods during M&A activity. That leaves them wide open to data breaches, compliance violations, and even deal cancellations.
So that’s where MailSPEC comes in.
As a regulatory solution company specializing in secure communication channels, we empower enterprises to communicate confidentially, efficiently, and in full compliance with legal and industry standards—even when two (or more) organizations with different security postures need to collaborate.
Let's break down nine practical ways to protect sensitive information during mergers and acquisitions with secure, compliant communication strategies.
When two companies start sharing data, their respective security standards rarely align perfectly. And that mismatch introduces vulnerabilities like:
Here, MailSPEC helps neutralize these risks by establishing secure communication protocols designed specifically for high-stakes, cross-organizational exchanges.
During M&A activity, teams often spin up new collaboration tools or rely on ad-hoc communication methods, which introduces risk and reduces accountability at the same time.
A better approach? Establish a secure, centralized policy for communication that includes:
This ensures everyone is on the same page—literally and digitally.
It may not be feasible to fully integrate both organizations' platforms during M&A discussions. And that’s also why MailSPEC offers temporary, secure messaging environments that:
This setup ensures that once the deal closes (or falls through), access can still be shut down with a single click.
Data shared during mergers and acquisitions may be subject to:
MailSPEC helps organizations meet these mandates by providing:
When parties from two or more organizations come together, verifying identities is critical. Using shared credentials or generic login links just will not cut it here.
Hence, to ensure integrity:
MailSPEC enables all of this through its secure user provisioning framework.
Encryption needs to be more than just "at rest" and "in transit." So, during M&A deals, every message and attachment MUST be end-to-end encrypted.
That means:
MailSPEC’s architecture is built around this level of encryption, ensuring the highest standards of M&A data protection.
Many data breaches happen when sensitive files are:
But with MailSPEC:
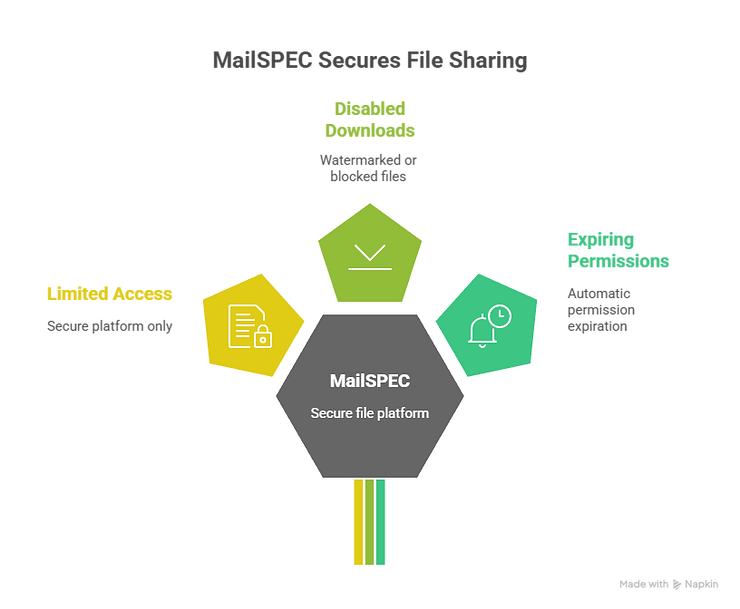
✔️ File access can be limited to the secure platform
✔️ Downloads can be disabled or watermarked
✔️ Sharing permissions can expire automatically
This locks down file access before, during, and after the deal.
You cannot protect what you can’t monitor. And that’s why communication transparency is essential.
MailSPEC provides:
These features help organizations detect anomalies early and as well as maintain a strong enterprise communication security posture throughout the M&A process.
The risks of poor communication security during M&A are very real. Here are two scenarios that could happen:
Imagine a healthcare organization sharing unencrypted patient data with a potential buyer via email. If that data were leaked, the deal could collapse, leaving the seller exposed to regulatory fines and even reputational damage, too.
Picture a tech merger where sensitive product roadmap discussions take place on a consumer messaging app. Say, if an employee were to leak that data, it could compromise their competitive edge and severely impact the merger's success as well.
Don’t let these risks become your reality. Secure your communication channels upfront.
MailSPEC is not just another secure messaging tool. It is a regulatory-focused communication solution that enables:
And whether you are initiating a merger, acquiring another firm, or simply preparing for due diligence, MailSPEC keeps your sensitive conversations safe and compliant.
Mergers and acquisitions are complicated enough. So do not let unsecured communication make them even riskier.
By establishing secure communication channels from day one, you:
✔️ Prevent unauthorized data access
✔️ Satisfy compliance requirements
✔️ Protect the value of the deal
And with MailSPEC, you can do it all without compromising usability or slowing down the process.
Let MailSPEC show you how to protect sensitive data, meet regulatory standards, and communicate confidently throughout the M&A lifecycle.
Contact us today for a tailored walkthrough of how our platform can secure your next big deal.
Ransomware attacks affect businesses no matter the size. You really don't want to know the average cost for recovering from a malicious ransomware attack... So what is a ransomware attack? A ransomware attack happens when malware (a virus) is deployed and then hold's the victim's information (on their own computer!) at ransom. This could be an individual user or an organization's valuable data; but made inaccessible by the owner! The hacker encrypts that data or holds it hostage and threatens the individual or organization with a ransom in order to either unlock the data or promise not to expose the hacked data.
Ransomware has experienced rapid growth because it's evolved from one-time attacks into a modern software-as-a-service business. Ransomware "organizations" have copied popular SaaS tech vendors and offer a highly polished product that relies on distributors to push the malware onto other people and machines in order for a cut of the ransom reward. Incredible as it sounds, real. An example of this is "phishing emails", which have embedded web links or attachments that infect your computer when you click on them. Ransomware is the fastest-growing malware hazard in the 21st century and in this article we are going to discuss three ways you can prevent a ransomware attack.
Did you know that it is estimated that nearly 3 out of 4 companies infected with ransomware suffer two days or more without access to their files.
Why should you continually update your software? Hackers love security flaws and spend time finding software vulnerabilities in programs. Software updates often include security patches that helps to cover known flaws or breeches in the programs that you and your employees use every day. In many ways, the learn by others mistakes so you do not have to do it yourself applies. So, be sure you are not left with vulnerable software that has already been compromised.Another risk from outdated software is the fact that security updates are not released after a product becomes obsolete. If a program you are using is obsolete, you may want to consider finding an alternative and removing that software program. The key takeaway is to make sure you or a cybersecurity expert assess the software programs you are using to make sure there are no known security vulnerabilities. Update or remove that outdated software.
Sometimes despite your best efforts at prevention, a breach is going to happen. Having a strong backup strategy, and a good restoration process in place ensures more protection against ransoms. Backups should always include offsite, that do not have direct connections to the network that might become infected. This allows restoration at a disaster recovery site, or replacement on the infected site, when the malware has been removed. As well as protecting against ransomware attacks, backups help protect your company against: - human errors, - hardware failures, - and power failures.
Humans are the most vulnerable point in your security system. Humans are lazy with passwords. A good way to check your password health is to use a service like NordPass to check the health of your passwords. NordPass will scan all your passwords saved in your vault and check how vulnerable they are. If you don't use a password vault like LastPass then you will have to manually ask yourself these questions.
💣 How complex are my passwords?
💣 Have I reused any passwords multiple times?
💣
Are any passwords over 90 days old?If you answered yes to any of these questions, you may need to look at changing some passwords. Another good thing to do is use multifactor authentication. The last blog post we wrote highlighted the importance of 2FA and MFA and would be good for you to review.
>> What is 2FA? A helpful Guide.
Did you know that 92% of malware attacks are delivered via email? A large % of those malware attacks are ransomware attacks first carried out through an email. Check out this list of trending CyberSecurity Statistics from 2021 for more details on that:
2021 Cyber Security Statistics Links and attachments are the two main ways a ransomware attack is carried out via email. It is a good idea for companies to train their employees to be aware of issues such as these and to fully audit their email and communications systems to see just how secure their company practices are.
Perhaps your email and communications systems need an audit to determine just how secure they are? MailSPEC offers System Audits where we review and provide recommendations for your email and voice communication systems. We provide honest reports, no matter the vendor or topologies used. Get in touch with us today at contact@mailspec.com for more information.
Two Factor Authentication or (2FA) shouldn't be overwhelming or something to be afraid of. 2FA simply makes your online accounts much more secure when you log in to them. You need to possess the password for your account as well as a means of verifying who you are.Simple right?Believe it or not, Two Factor Authentication first emerged in 1986 in the form of a key fob... Now things have certainly changed a bit since those days and in this blog post, we are going to break down 2FA for you and make it easy to understand.
Let's start at the very beginning. In order to create an account online, whether that's email, social media, subscription or a bank account, you need to create a log in. This login generally requires a username, password, and/or an email address. This is the first layer of security.
Seeing as how you don't want anyone else to have access to your account, you create a username and a password unique enough so only you can log in. Here are two big reasons why the first layer is not good enough for security purposes. 1 - You use the same password for multiple accounts. This is a security risk because hackers LOVE password recycling. Security breaches happen all the time and if you re-use the same password everywhere all it takes is one account to be hacked and all your accounts will give the hacker access. 2 - Humans get tired and lazy. It takes effort to create unique passwords and remember them. You either need to find something like LastPass or have an amazing memory. When you get annoyed with remembering passwords you get lazy in order to make it easier on yourself. This sets you up to be hacked easier. Two Factor Authentication is an extra layer of security that makes it that much harder for hackers to access your private accounts. Microsoft shared an incredible report from 2019 that concluded 2FA blocks 99.9% of automated hacker attacks. A similar report from Google had the same conclusion.
The following forms are the most common 2FA methods.
It really isn't that difficult to set up two factor authentication. As mentioned previously the first layer is your password. The most common second layer of security is your smartphone. In 2022 almost everybody owns a smartphone making it pretty straightforward to set up 2FA.
Your smartphone assists with the second layer of security in one of two ways.
Sounds pretty simple right?
"True Cybersecurity is preparing for what's next, not what was last." – Neil Rerup
Let's break down which service you should protect with 2FA.
You probably have hundreds of accounts across the internet, anything from Amazon to Google to Facebook to your local pizza shop. Which accounts need 2FA? Well let's get this right out of the way, any account that supports 2FA would be a good one to protect! We'd recommend starting with the following accounts. 1 - Bank / Finance Related2 - Password Managers3 - Google, Microsoft, and Apple Accounts4 - Social Media Accounts5 - Shopping and Commerce Accounts
Yes, that's quite a few accounts... So how do you actually set up 2FA with your smartphone?
Here's the good news, setting up your second layer of security via 2FA with a smartphone is very very easy.
-- Method 1 -- SMS Messages
Let's use Twitter as an example. 1 - Select MORE (three dots in a circle in the bottom left of your screen)2 - Select Security and account access3 - Select Security You'll see this screen.
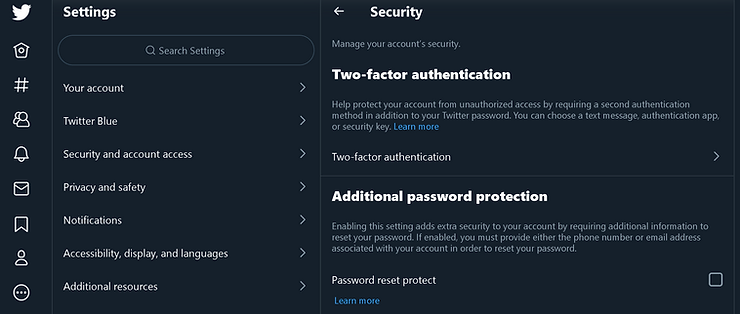
Now select Two Factor Authentication.You will see the following screen.
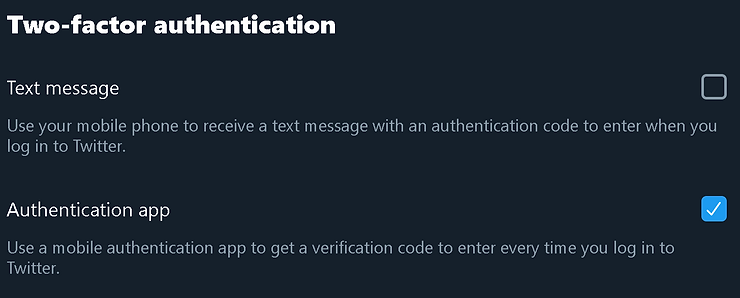
You can choose either text message(SMS) or use an Authentication app. In this method, we are using SMS so select that. Now you just need to input your mobile number and tap OK. You will now receive an SMS message from Twitter with a six-digit code. Enter the code into Twitter and viola your 2FA setup is DONE! Now in order for someone to access your Twitter account, they'd need your password as well as your 2FA 6 digit code.
-- Method 2 -- Authenticator App
To make use of an authenticator app you will need to still an app on your smartphone. There are a few options for you depending on the device you use. Here are a few. Google & Microsoft Authenticator - both highly used and reliableAuthy - very easy to useLast Pass Authenticator App - if you use LastPass for your passwords this is a great optionandOTP - open-source alternativeactiveauth - a MailSPEC product! 2FA and MFA or Multi-Factor Authentication is native to our core products. We provide biometric control over web access for our users and activeauth is integrated to 3rd party applications with OTP support. The mobile experience is seamless for a transition to higher security on a private system that is easy to use and onboard.
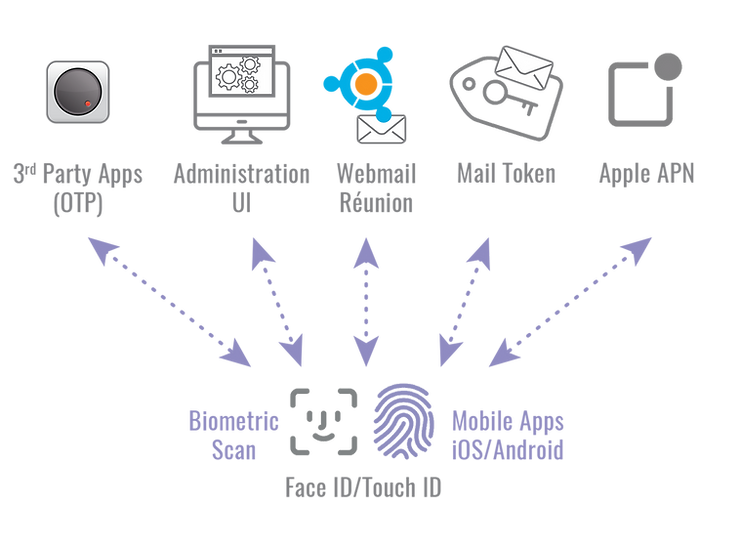
Once you've downloaded the app you are ready to use the authenticator app as a form of 2FA. Let's use Twitter again as an example. 1 - Select MORE (three dots in a circle in the bottom left of your screen)2 - Select Security and account access3 - Select Security You'll see the same screen as the last steps. Select Two Factor Authentication again. This time though, select Authentication App. This popup will appear.
Select get started.
Now using your authentication app, select add a new account and then scan this code using your smartphone camera! The app will do the rest. Once the account is setup it will begin generating codes for you every so often. This randomization really ups the security with 2FA!Now there's one last step! You need to enter the current 6 digit code from the authenticator app into Twitter. Simply enter it below and viola, you have set up 2FA with an authentication app.
Two Factor Authentication increases your online security by adding a second layer of security to keep hackers at bay. We hope this blog post has been helpful for you, follow us on LinkedIn and Twitter for all things Cybersecurity, and stay tuned for more helpful blog posts from the Cybersecurity world.
News about new releases of MailSPEC products and services.
June 2nd, 2026: MailSPEC today officially released PassLink 3, the enterprise-grade, on-premises secure file-sharing platform purpose-built for organizations that must exchange sensitive documents with customers, partners, suppliers, and citizens while maintaining full sovereign control and regulatory compliance.
Designed for finance, healthcare, insurance, government agencies, legal practices, and critical infrastructure, PassLink 3 delivers military-grade quantum-safe encryption, authenticated access receipts, automated audit trails, time-limited expiration, and seamless SDK integration into CRM, ERP, and billing systems, all without forcing users to abandon the familiar email workflows they already use.
In 2026, the majority of regulated organizations still rely on ordinary email or free consumer cloud links (Google Drive, Dropbox, WeTransfer, OneDrive) to send invoices, lab results, insurance claims, passport scans, legal contracts, and government notices. This practice is now a documented regulatory and security disaster.
A doctor emails lab results containing patient names, diagnoses, and test values to a patient’s personal Yahoo or Gmail account. The email is unencrypted, stored indefinitely on foreign servers, and can be forwarded, intercepted, or subpoenaed without the healthcare provider’s knowledge. This instantly violates HIPAA’s Security Rule (transmission security) and Privacy Rule (minimum necessary standard). U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) has repeatedly fined organizations for exactly this behavior. One recent settlement reached $9.76 million for repeated email security failures involving protected health information (PHI). Another provider was hit with a $3 million penalty after unencrypted PHI emails were sent to the wrong recipients.
An insurance company emails policy documents or claims forms to a customer’s Gmail address. The attachment contains personally identifiable information (PII) and protected health information. The email sits in the recipient’s inbox forever, can be downloaded by anyone with access to that account, and creates an untraceable chain of custody. When regulators or auditors request proof of secure transmission and receipt, the company has none.
A tax authority or social services agency emails sensitive benefit letters, ID verification requests, or passport scan requirements to citizens using Yahoo or Hotmail. The files leave sovereign jurisdiction the moment they are sent, violating national data-localization laws and exposing citizens to foreign government access requests under laws like the U.S. CLOUD Act.
These are not theoretical risks. They are daily occurrences that regulators are now punishing aggressively.
In Europe, GDPR enforcement in 2025 alone generated over €1.2 billion in fines, with many stemming from insecure data transfers and email-based sharing failures. In Japan, the Act on the Protection of Personal Information (APPI) now carries penalties up to ¥100 million per violation for improper handling or transfer of personal data outside approved jurisdictions.
The core problem is simple: consumer email and cloud services were never built for regulated file sharing. They offer zero control over:
The result is broken chains of custody, massive regulatory exposure, and constant risk of industrial espionage or data breaches.
PassLink 3 solves every one of these problems by keeping 100 % of the file lifecycle inside the organization’s sovereign perimeter (on-premises or approved sovereign cloud). No data ever touches foreign consumer services.
Every file is encrypted end-to-end with post-quantum cryptography before it leaves the sender’s system. Even if an attacker intercepts the transmission or compromises the recipient’s device years from now, the file remains unreadable. This directly addresses “harvest now, decrypt later” threats that regulators and security agencies are now mandating protection against.
Recipients must authenticate (via secure link + one-time code or organizational credentials) before they can even see the attachment. Upon opening, PassLink 3 instantly generates a tamper-proof receipt that logs:
All activity is recorded in an immutable WORM archive on the sender’s sovereign infrastructure. Auditors and regulators can retrieve a complete, court-admissible trail in seconds.
Legal and compliance teams create branded templates with automatic disclaimers (“This document contains personal data protected under GDPR/APPI/HIPAA – unauthorized forwarding prohibited”), return receipt requirements, and jurisdiction-specific warnings. Templates are stored centrally and applied automatically via the SDK.
One of PassLink 3’s most powerful innovations is “Reverse Onboarding.” Legal firms, insurance adjusters, government agencies, and healthcare providers can send a one-click secure link to clients using ordinary Gmail or Yahoo addresses. The recipient clicks, authenticates once, and gains a temporary, fully controlled portal to upload or view documents, without ever needing to install anything or change their email habits.
This is revolutionary for:
Claims adjusters request medical records, accident photos, or ID scans from policyholders. The policyholder uploads directly into the secure session; everything is encrypted, audited, and stays inside the insurer’s sovereign environment. No more “please email us your passport scan” disasters.
Lawyers handling divorce, estate planning, or corporate transactions send sensitive contracts and identification documents to clients via consumer email. Clients upload passport scans or financial statements through the authenticated portal. Everything remains under the law firm’s jurisdiction and audit control.
Tax offices or benefits administrators send citizens secure links to upload supporting documents. The citizen authenticates, uploads, and receives an instant receipt. All files stay inside the government’s sovereign infrastructure, satisfying strict localization requirements in Japan, the EU, and the GCC.
PassLink 3’s SDK allows developers and IT teams to embed secure file exchange directly into existing CRM, ERP, billing, and case-management platforms. No separate portal. No user training.
Under the Economic Security Promotion Act and APPI, organizations must keep critical personal and business data inside Japanese jurisdiction. PassLink 3’s on-premises deployment ensures files never leave Japanese soil or approved sovereign clouds. Companies in manufacturing, fintech, and healthcare can now safely share technical drawings, patient records, or supply-chain contracts without risking foreign jurisdiction exposure.
NIS2, the EU AI Act, and GDPR require demonstrable control over data transfers. PassLink 3 provides the missing piece: sovereign encryption + immutable audit trails that satisfy supervisory authorities in Germany, France, and Ireland. Organizations avoid the €20 million+ fines that have become routine for unsecured data sharing.
Vision 2030 programs and national data-localization laws demand that citizen and corporate data remain under local control. PassLink 3 enables government agencies and private enterprises to distribute benefits documents, insurance policies, or legal notices while keeping every byte inside approved borders.
Every file transaction generates a complete, cryptographically signed audit log that includes:
Compliance officers and external auditors can export reports in seconds, turning what was previously a months-long forensic nightmare into an instant regulatory checkbox.
Consumer email and free cloud buckets were convenient yesterday. Today, compliance time bombs can expose organizations to billion-dollar fines, data breaches, and loss of sovereign control. PassLink 3 removes the risks with a secure, auditable, quantum-safe pipeline that works exactly where your staff and customers already are. Your data. Your jurisdiction. Your control.
Contact MailSPEC today for a no-risk TestFlight. Stop sending sensitive documents into the unknown.
[1] HIPAA Journal – “Is it a HIPAA Violation to Email Patient Names?” (2026 Update)
https://www.hipaajournal.com/is-it-a-hipaa-violation-to-email-patient-names/
[2] LuxSci – “Can You Send PHI Through HIPAA Email?”
https://luxsci.com/can-you-send-hipaa-through-email/
[3] Paubox – “HIPAA Compliant Email: The Definitive Guide (2026 Update)” – Solara $9.76M settlement
https://www.paubox.com/blog/hipaa-compliant-email
[4] HIPAA Times – Top HIPAA email violations including Solara $3M fine
https://hipaatimes.com/top-5-hipaa-email-violations-and-how-to-avoid-them
[5] Surfshark – “GDPR breaches led to over €1B in fines in 2025”
https://surfshark.com/research/study/gdpr-fines-2025
[6] Endpoint Protector – “Data Protection in Japan: All You Need to Know about APPI” – ¥100M maximum fines
https://www.endpointprotector.com/blog/data-protection-in-japan-appi/
[7] UnitedLayer – “Sovereign Cloud Explained” – data residency and quantum-safe controls
[8] OPSWAT – “The Future of Secure File Transfer – AI, Quantum & Zero Trust”
https://www.opswat.com/blog/the-future-of-secure-file-transfer-ai-quantum-and-zero-trust
May 5th, 2026: MailSPEC today officially released EasyCrypt 3, the groundbreaking client-side encryption and AI governance platform engineered for organizations that must repatriate sensitive data into full sovereign control while continuing to communicate securely with external parties on consumer email systems.
EasyCrypt 3 is not another email encryption tool. It is a comprehensive compliance engine that runs 100% on-device and on-client, classifying data in real-time using an AI policy engine tailored for national regulations or organizational rules. It applies quantum-safe end-to-end encryption and enables secure external sharing without ever transmitting raw data to foreign clouds. The result: regulated enterprises and government agencies can finally repatriate thousands of sensitive emails and attachments from Microsoft 365, keep everything under local jurisdiction, and still exchange documents safely with customers, partners, and citizens using ordinary Gmail, Yahoo, or Hotmail addresses.
The Problem: Legacy Email Encryption and Consumer Systems Are Breaking Sovereignty and Compliance
For decades, organizations in finance, healthcare, and national security have tried to use legacy email encryption (PGP, S/MIME, or Microsoft 365 encryption) and public cloud storage. These approaches create three fatal flaws that regulators now punish aggressively.
First, traditional encryption happens without data classification, and the keys are managed on the user’s desktop, or worse, in a gateway device that is subject to attack. The endpoint (laptop, phone, or server) holds the keys, and key management becomes a nightmare for compliance teams. Auditors cannot prove who had access or when the data was decrypted.
Second, most situations result in plaintext or encrypted copies at rest on foreign clouds (Microsoft, Google, Yahoo), exposing organizations to CLOUD Act requests, GDPR international transfer violations, and “harvest now, decrypt later” quantum risks.
Third, when organizations need to repatriate data from Office 365 or consumer platforms, they face months of manual effort with no automated classification or audit trail.
Real-world consequences are severe. In 2025–2026 alone, GDPR enforcement generated more than €1.2 billion in fines, many tied to insecure email transfers and loss of control over personal data. HIPAA violations involving email transmission of PHI (Personal Healthcare Information) have produced settlements in the millions, including a $9.76 million penalty against one provider for repeated unsecured email failures. Japanese APPI enforcement now carries penalties up to ¥100 million for improper handling or transfer of personal data outside approved jurisdictions.
Government agencies using Microsoft 365 face the same crisis. Emails and attachments containing classified information, citizen records, or proprietary intelligence often sit in U.S.-controlled clouds with no guarantee of sovereignty. When these agencies need to share documents with citizens on Gmail or partners on Yahoo, the data immediately leaves national jurisdiction, creating unacceptable breaks in the chain of custody.
EasyCrypt 3 solves these problems at the source. The platform’s revolutionary on-device AI Governance Engine performs data classification and policy enforcement before any transmission occurs. The AI-powered policy engine allows compliance teams to create country-specific or organization-specific rules that run entirely on the client device, Mac, Windows, iOS, or web, with zero raw data ever leaving the sovereign perimeter.
Unlike legacy technology that only encrypts content after it has already been typed or attached, EasyCrypt 3’s Local AI Governance and classification engine scans every message or draft in real time using locally stored models. It detects sensitive patterns (PHI elements, trade secrets, classified keywords, export-controlled references) and applies the correct data classification and policy instantly. No cloud AI calls. No data exfiltration. Full explainability logs for regulators.
This on-client approach is fundamentally different from legacy systems. Traditional encryption tools hand control to the endpoint or cloud provider. EasyCrypt 3 keeps control of the organization at every step.
EasyCrypt 3 uses NIST-approved post-quantum algorithms combined with a patented hybrid encryption scheme protecting data both in transit and at rest. This eliminates the “harvest now, decrypt later” threat that security leaders now rank as a board-level priority. Even if an attacker captures encrypted traffic today and waits for quantum computers in 2035 or beyond, the data remains unreadable.
The system’s patent-pending key management architecture ensures that decryption keys never leave the sovereign environment. Compliance officers retain full control, with automated rotation and escrow that satisfies the strictest audit requirements.
Government agencies and regulated enterprises using Office 365 can now repatriate years of sensitive emails and attachments in weeks instead of years. EasyCrypt 3’s desktop client (Windows, macOS) and Outlook add-in scan existing mailboxes on-device, classify every message and attachment according to custom policies, apply quantum-safe encryption, and migrate the data to the organization’s on-premise or sovereign-cloud archive, all without ever sending raw content outside the jurisdiction. One European government ministry recently completed the repatriation of 1.2 million classified emails and attachments in 38 days, achieving full NIS2 and sovereign compliance with zero foreign-risk findings.
Secure External Sharing Without Foreign Cloud Exposure
When sending to external recipients on Gmail, Yahoo, or Hotmail, EasyCrypt 3 creates a secure, authenticated portal link. The recipient authenticates once (no app download required) and views the message and attachments in a browser session that never stores data on foreign servers. The entire session is encrypted end-to-end, logged with tamper-proof receipts, and can be revoked or expired at any time. The raw data never leaves the sender’s sovereign infrastructure, solving the impossible dilemma that has plagued regulated organizations for years.
An insurer sends policy documents containing medical history to a claimant using Gmail. The claimant clicks the secure link, authenticates, views the watermarked document, and uploads required ID scans back through the same session. Everything
remains inside the insurer’s jurisdiction and is fully auditable.
A tax authority sends benefit verification requests or passport scan instructions to citizens via consumer email. Citizens upload documents through the authenticated portal; all files stay encrypted and under government control.
Full Integration Across the Enterprise Ecosystem
EasyCrypt 3 is natively integrated into:
The new EasyCrypt SDK allows seamless embedding into Oracle NetSuite, SAP, and other ERP/CRM systems. Finance teams can trigger classified communications directly from billing workflows; healthcare providers can release lab results from EHR systems; legal departments can attach contracts from case-management platforms, all with automatic classification, quantum-safe encryption, and audit trail journaling.
Banks and investment firms must comply with MiFID II, SEC rules, and Japanese FSA requirements while protecting proprietary trading strategies. EasyCrypt 3 enables safe repatriation from Office 365 and secure sharing with clients on consumer email, all while feeding classified conversations into private AI models for KYC/AML analysis without leakage.
Providers can repatriate years of PHI-laden emails, classify new messages on-device, and share lab results or discharge summaries with patients on Gmail without breaking HIPAA or GDPR chains of custody.
Agencies repatriate sensitive Office 365 mailboxes, maintain air-gapped archives, and communicate securely with external partners or citizens while keeping every byte under sovereign control.
“EasyCrypt 3 is the missing link for regulated markets,” said Chukri, Senior Technical Lead, Protocols, SDK, and Compliance Technologies at MailSPEC. “For the first time, organizations can repatriate sensitive data into true sovereign control while continuing to operate with the tools their people already know. The new SDK will drive wider adoption across financial services, allowing teams to embed sovereign classification directly into KYC/AML workflows. Compliance stops being a burden and becomes a strategic advantage that powers innovation without risk.”
The convergence of the EU AI Act (full enforcement August 2026), Japan’s updated Cybersecurity Strategy and Active Cyber Defense Law, NIS2, DORA, APPI amendments, and U.S. quantum-readiness mandates has created an urgent requirement: organizations must prove they control their data, can classify it automatically, and can share it securely without foreign exposure.
EasyCrypt 3 delivers exactly that capability in a single, intuitive platform. It repatriates what is already in the cloud, protects what is being created today, and enables safe external collaboration tomorrow, all with on-device AI governance, quantum-safe cryptography, and seamless integration across the tools organizations already use.
Contact MailSPEC today for a sovereign repatriation TestFlight. Stop sending sensitive information into the unknown.
[1] Cogent Information Technologies – “Quantum-Safe Cryptography: The 2026 Mandate to Future-Proof Enterprise Data” (January 2026)
[2] Level.io – “Quantum-Safe Encryption Explained for MSPs and IT Teams” (March 2026)
https://level.io/blog/quantum-safe-encryption
[3] World Economic Forum – “Why quantum security is a question leaders cannot ignore right now” (February 2026)
https://www.weforum.org/stories/2026/02/quantum-security-question-leaders-cannot-ignore/
[4] DLA Piper – “GDPR Fines and Data Breach Survey: January 2026” (aggregate €1.2 billion in 2025)
[5] HIPAA Journal – “What are the Penalties for HIPAA Violations? 2026 Update” (including $9.76M settlement example)
https://www.hipaajournal.com/what-are-the-penalties-for-hipaa-violations-7096/
[6] Endpoint Protector – “Data Protection in Japan: All You Need to Know about APPI” (¥100M maximum fines)
https://www.endpointprotector.com/blog/data-protection-in-japan-appi/
[7] Databalance – “Microsoft Cloud sovereignty in 2026: ambition and reality” (M365 Local repatriation and sovereignty trends)
https://www.databalance.eu/en/microsoft-cloud-sovereignty-2026/
[8] MDaemon Blog – “Migration Case Studies: Moving Email from Microsoft 365 back on-premises” (sovereignty and compliance drivers)
https://blog.mdaemon.com/migration-case-studies-moving-email-from-microsoft-365-back-on-premises
[9] Deloitte – “2026 Global Insurance Outlook: Digital Transformation and Data Sovereignty” (secure external sharing and compliance in insurance)
[10] SDK.finance – “Integrations” (SDK examples for KYC/AML and ERP systems)
Paris - April 14, 2026 — MailSPEC today officially released CommuniGate SPEC 8.1, the next-generation on-premise sovereign email and unified messaging platform engineered specifically for organizations that demand complete jurisdictional control, regulatory compliance, and ironclad security.
Built from the ground up for finance, healthcare, government agencies, intelligence services, defense contractors, and critical infrastructure operators, CommuniGate SPEC 8.1 delivers enterprise governance, true sovereign data control, advanced security protections, immutable audit trails, and full support for air-gapped topologies, all while providing the reliability, scalability, and familiar user experience that organizations require.
CommuniGate SPEC 8.1 introduces several powerful enhancements focused on security, usability, compliance, and secure collaboration:
Across regulated industries, employees have migrated sensitive communications to unauthorized consumer messaging apps and public-cloud email services. What began as convenience has become a systemic vulnerability.
In the United States alone, the Securities and Exchange Commission (SEC) and Commodity Futures Trading Commission (CFTC) have imposed more than $3.5 billion in cumulative fines on Wall Street firms since 2021 for failing to preserve records of business communications conducted on unauthorized messaging apps and non compliant email platforms.
The landmark case that set the tone was JPMorgan Chase’s $200 million penalty in December 2021 for widespread use of WhatsApp and personal devices. Subsequent waves hit 16 major firms with $1.1 billion in September 2022, followed by another $549 million in 2023 and $81 million in 2024. The message from regulators is unmistakable: using non-compliant tools is no longer a minor policy violation; it is a multi-million-dollar regulatory landmine.
In Europe, the risks are equally severe. Ireland’s Data Protection Commission (DPC) levied a €225 million GDPR fine on WhatsApp itself in 2021 for transparency violations, a penalty upheld through multiple appeals and one of the largest data protection fines in history. European banks and public-sector bodies face mounting pressure under NIS2, the EU AI Act, and national sovereignty mandates.
In Japan, regulators have taken a hard line. The Financial Services Agency (FSA) has conducted raids and issued business-improvement orders on apps like LINE for compliance failures involving customer data. Japanese banks and government agencies are under strict obligations to prevent foreign jurisdiction exposure under the Economic Security Promotion Act and the Society 5.0 framework.
These cases reflect a global pattern: consumer messaging apps and foreign cloud email services were never designed for regulated or classified environments. They store metadata and content on external clouds, lack immutable audit trails under your control, cannot guarantee jurisdictional sovereignty, and expose organizations to CLOUD Act requests, GDPR violations, and national-security breaches.
Enforcing a minimum (“floor”) TLS version combined with post-quantum cryptographic algorithms protects against downgrade attacks and future quantum computing threats. Quantum computers are expected to eventually break current public-key encryption algorithms (such as RSA and ECC) using Shor’s algorithm. Post quantum cryptography ensures long-term confidentiality of sensitive data that must remain secure for decades, especially critical for defense contractors and national security agencies handling classified information.
This feature directly counters “harvest now, decrypt later” strategies, where adversaries collect encrypted traffic today with the intent of decrypting it once quantum computers become available. It aligns with NIST’s finalized post-quantum standards and U.S. national security requirements for protecting data with decades long sensitivity.
The new auto-blacklist capability automatically detects and blocks IP addresses showing suspicious behavior such as repeated failed logins, spam patterns, or brute force attempts. This proactive defense significantly reduces inbound spam, lowers the risk of phishing and malware delivery, improves server performance, and helps maintain a clean reputation for outbound email, all without manual intervention.
For organizations handling classified information or operating in high-security environments, running your own on-premises or air-gapped email infrastructure like CommuniGate SPEC 8.1 is often the only acceptable option. Key strategic advantages include:
In Europe, the NIS2 Directive raises cybersecurity requirements across 18 critical sectors and emphasizes data sovereignty and risk management for network and information systems. On-premises solutions help organizations achieve the directive’s goals of enhanced resilience and reduced dependence on foreign cloud providers.
In Japan, the Economic Security Promotion Act treats data protection as a matter of national security, imposing strict screening and localization requirements for critical infrastructure and sensitive information. Self-hosted systems provide the jurisdictional independence and control demanded by these frameworks.
Industry analysis confirms that self-hosted sovereign email infrastructure provides the tighter control, auditability, and isolation essential for defense, intelligence, critical national infrastructure, and regulated sectors under NIS2 or Japan’s Economic Security Promotion Act.
CommuniGate SPEC 8.1 integrates seamlessly with Office 365, Oracle NetSuite, SAP, and other systems. Repatriation tools scan U.S.-cloud data, apply policy classification, and transfer it to sovereign infrastructure while maintaining integrity at rest.
The era of outsourcing critical digital infrastructure is over. France’s sovereign mandates, Japan’s Economic Security Act, GCC localization laws, and U.S. defense requirements mark the beginning of a global shift. MailSPEC’s CommuniGate SPEC 8.1 lets you keep the intuitive email and messaging experience users love while adding invisible governance, quantum-safe security, sovereign integrity, and instant compliance tools.
Contact MailSPEC today for a test flight in Europe, Japan, the GCC, or North America.
[1] LeapXpert – Electronic Messaging Compliance and Regulatory Fines Summary (2023–2025 updates)
https://www.leapxpert.com/electronic-messaging-compliance-investigation-and-regulatory-fines summary/
[2] CNBC – JPMorgan fined $200 million for WhatsApp use (December 2021)
https://www.cnbc.com/2021/12/17/jpmorgan-agrees-to-125-million-fine-for-letting-employees-use whatsapp-to-evade-regulators.html
[3] The New York Times – Texting on Private Apps Costs Wall Street Firms $1.8 Billion (September 2022)
https://www.nytimes.com/2022/09/27/business/banks-fined-texting-sec.html
[4] Reuters – Big banks expected to rack up more than $1 billion in fines for WhatsApp use (2022) https://www.reuters.com/business/finance/big-banks-expected-rack-up-more-than-1-bln-fines whatsapp-use-2022-08-22/
[5] Termly – 61 Biggest GDPR Fines (WhatsApp €225 million Ireland DPC, 2021, upheld 2026) https://termly.io/resources/articles/biggest-gdpr-fines/
[6] EFF – After Years of Controversy, the EU’s Chat Control Nears Its Final Hurdle (December 2025) https://www.eff.org/deeplinks/2025/12/after-years-controversy-eus-chat-control-nears-its-final hurdle-what-know
[7] Business Times Singapore – Japan regulators raid messaging app Line (historical context of FSA scrutiny)
https://www.businesstimes.com.sg/startups-tech/technology/japan-regulators-raid-messaging-app line-over-use-payment-tokens
[ 8] Spamhaus – Six advantages to running your own email server (control over data, privacy, and jurisdiction)
https://www.spamhaus.com/resource-center/six-advantages-to-running-your-own-email-server/
[9] Federal News Network – Why a self-hosted collaboration platform is essential for digital sovereignty and incident response (air-gapped, government use cases)
https://federalnewsnetwork.com/commentary/2023/07/why-a-self-hosted-collaboration-platform-is essential-for-digital-sovereignty-incident-response/
[10] MailSPEC – Why Self-Hosting Your Email Server is Essential for Sovereignty (2025) https://www.mailspec.com/post/why-self-hosting-your-email-server-is-essential-for-sovereignty
[11] Huntress – What Is On-Prem Security and Why It Still Matters (defense, data sovereignty, compliance)
https://www.huntress.com/cybersecurity-101/topic/what-is-on-prem
[12] Spectro Cloud – Sovereign compute infrastructure for defense & government (air-gapped environments)
https://www.spectrocloud.com/government/sovereign-compute
[13] Cisco – Sovereign Critical Infrastructure Portfolio (air-gapped on-prem for Europe and defense) https://newsroom.cisco.com/c/r/newsroom/en/us/a/y2025/m09/cisco-announces-sovereign-critical infrastructure-portfolio.html
[14] Oracle – Sovereign Air-Gapped Cloud Offering for national security
https://www.oracle.com/news/announcement/oracle-advances-national-security-with-new-sovereign air-gapped-cloud-offering-2025-06-17/
[15] European Commission – NIS2 Directive: securing network and information systems https://digital-strategy.ec.europa.eu/en/policies/nis2-directive
[16] METI Japan – Economic Security Promotion Act and data protection requirements https://www.meti.go.jp/english/report/data/wp2023/pdf/2-1-2.pdf
MailSPEC Unveils JACE Version 3: Sovereign Client-Side AI Delivers Unmatched Compliance, Data Sovereignty, and Audit Readiness for Regulated Industries
April 7, 2026 – MailSPEC, the innovator in governance and intelligent compliance technology for communications today announced the general availability of JACE Version 3, its compliance classification AI engine engineered exclusively for the world’s most regulated sectors. Built as an on-client (End to End Encryption), zero-cloud data transfer, and multi-channel (email, chat, video, file classifier) solution, JACE solves the dilemma for strong regulatory compliance, while protecting privacy in Sovereign deployment.
JACE 3 (Journaling, Archival, Compliance, and Escrow) provides a new SDK, with a programming interface powered by “JACE Policy Script” to enable Compliance officers and CISO’s to fine tune the policy for each business process or regulatory requirement. Seamless integrations with Office365, Oracle NetSuite, SAP, Finance application and National Security software are unique, and set the Compliance platform apart in its ability to adapt to different regulatory policy or industry applications.
JACE 3 empowers banks, healthcare providers, governments, and multinational enterprises to harness AI without compromising the confidentiality of their most valuable asset: internal proprietary data and business “know how”. Internal communications contain the “secret sauce” of the organization for competitive advantage and privacy,; especially that of the customer data sets entrusted.
In an era of escalating regulatory scrutiny and geopolitical data risks, JACE 3 stands as the definitive solution for organizations that refuse to send sensitive information to Cloud or public LLMs. The platform processes every AI task entirely on-deck or “client-side”, ensuring end-to-end encryption and complete data sovereignty from ingestion to audit trail.
“Internal communication data is the crown jewel of any organization, its intellectual property, customer records, trading strategies, patient histories, and strategic plans,” said Tanguy Godquin Phd, Director of Research and Development at MailSPEC. “JACE 3 does not just protect that data; it actively discovers, classifies, and governs it using policy-driven metadata indexing. No other solution delivers enterprise-grade AI compliance with zero risk of exfiltration.”
At the heart of the release is sovereign client-side AI governance engine. Unlike “cloud dependent” compliance tools that require uploading sensitive documents to remote servers, JACE 3 runs its advanced policy models directly on the organization’s infrastructure or end-user devices. Sensitive information never leaves the client environment. This architecture eliminates the single greatest compliance risk in regulated industries: unintended data transfer to foreign jurisdictions or third-party LLMs.
JACE 3 introduces a powerful Software Development Kit (SDK) that enables frictionless integration with mission-critical systems, including:
Developers can embed JACE intelligence into existing workflows in days, not months, using secure APIs that maintain full encryption boundaries.
JACE 3 employs proprietary detection algorithms to identify proprietary and regulated data in real time; whether in emails, attachments, chat logs, ERP entries, or document repositories. Once detected, the classification engine applies organization specific policies to automatically:
This capability transforms compliance from a reactive burden into a proactive strategic advantage. Financial institutions can now prove adherence to MiFID II, SOX, SEC rule 17a and Japanese requirements with click-of-a-button reports. Healthcare organizations achieve effortless HIPAA , GDPR, APPI and National healthcare alignment while accelerating clinical research workflows.
The demand for sovereign AI solutions is no longer niche, it is a strategic necessity. Geopolitical tensions, extraterritorial laws such as the U.S. CLOUD Act, and stringent regional regulations have accelerated the adoption of data localized technologies. According to Grokipedia’s [1] comprehensive “2026 in Information Technology” entry, organizations are increasingly prioritizing data sovereignty and private AI deployments to process sensitive information without relinquishing control to third-party infrastructure. Deloitte forecasts nearly US$100 billion in global investment in sovereign AI compute during 2026 alone, driven by the need to build localized infrastructure outside major hyperscaler dominance.
In the European Union, the EU AI Act [2] (fully enforceable August 2026) and the EU Data Act [3] have made digital sovereignty a cornerstone of industrial policy. Enterprises face fines up to 7% of global turnover for non-compliance, while initiatives like Gaia-X [4] promote federated, EU-centric infrastructure. Over 75% of enterprises in Europe and the Middle East are projected to adopt “geo repatriation strategies, shifting workloads to sovereign or regional clouds, by 2030, per Gartner projections [5] cited in industry analyses.
The GCC region is following suit. National strategy vision in the Kingdom of Saudi Arabia, UAE, and Qatar now mandate localization for government, healthcare, and financial data. As PwC’s 2026 economic outlook notes [6], data sovereignty will increasingly shape AI deployment, with regulators expected to require domestic infrastructure for sensitive workloads.
Japan continues its steady push toward technological self-reliance under the Act on the Protection of Personal Information(APPI) [7] and growing emphasis on secure AI infrastructure. Collaborative efforts such as the EU-Japan Digital Week [8] between the European Union and Japan highlight data sovereignty and FAIR data principles as foundational for trusted cross-border partnerships. The EU-Japan Digital Partnership [9] (launched in 2022) serves as a major platform for collaboration; bringing together stakeholders from government, industry, academia, research, and policymaking agencies.
For Japan, the adoption of sovereign client-side AI solutions such as MailSPEC’s JACE Version 3 is not merely a technological upgrade, it is a strategic necessity for national security, regulatory compliance, and economic resilience. In December 2025, Japan’s Cabinet adopted a new five-year Cybersecurity Strategy [10], which explicitly recognizes state-sponsored cyberattacks from adversaries as “serious security threats” and shifts toward proactive defense and deterrence, including active cyber defense (ACD) measures implemented through joint public-private efforts and international cooperation (National Cybersecurity Office, Cabinet Secretariat, Outline of the Cybersecurity Strategy, December 23, 2025) [10]. This builds directly on the landmark Active Cyber Defense Law [10], enacted on May 16, 2025, and set for phased full implementation by 2027, which empowers authorities, including police and Self-Defense Forces to neutralize threats preemptively, utilize communications data under safeguards, strengthen public-private collaboration via a new Cyber Council, and reorganize structures for enhanced response capabilities (Japan Active Cyberdefense Law enactment reports, May-August 2025; Baker McKenzie analysis, January 22, 2026) [10].
At the same time, Japan continues to tighten data protection frameworks under the Act on the Protection of Personal Information (APPI). Ongoing reviews and anticipated amendments in 2026 focus on strengthening individual rights, enhancing enforcement (including potential administrative monetary penalties), refining cross-border data transfer rules, and addressing AI-related risks, all while promoting responsible data use amid growing concerns over extraterritorial exposure and supply-chain vulnerabilities (Personal Information Protection Commission Policy Direction for Amendment of the APPI, January 9, 2026) [11].
Japan’s most valuable assets, financial trading data, healthcare records, intellectual property, and government secrets, must remain under absolute Japanese control to mitigate risks from foreign subpoenas, geopolitical coercion, or industrial espionage breaches. Cloud-based AI systems inherently require uploading sensitive information to external systems, creating unacceptable vectors for exfiltration. JACE’s on-deck or fully client-side architecture eliminates this: no sensitive data ever leaves the organization’s perimeter, while end-to-end encryption and policy-driven metadata indexing automatically detect proprietary content, apply retention and audit rules, and generate immutable trails for eDiscovery and regulatory audit trails. JACE 3 is fully aligned with APPI restrictions and the new cybersecurity mandates.
This imperative is further evidenced by industry actions, such as Fujitsu’s February 2026 announcement of manufacturing “Made in Japan” sovereign AI servers at its Kasashima Plant, starting in March 2026, featuring leading-edge processors and confidential computing for mission-critical operations under domestic jurisdiction (Fujitsu Group press release, February 12, 2026). In regulated sectors like banking, healthcare, and national defense, only client-side AI delivers powerful intelligence without surrendering Sovereignty. As Japan accelerates technological self-reliance amid rising AI-driven cyber risks and state-level threats, JACE provides the secure, auditable foundation that safeguards the nation’s data crown jewels while enabling responsible AI innovation; precisely the balance demanded by Tokyo’s evolving cybersecurity, data-protection, and economic security framework.
In regulated industries, government agencies, and national security contexts, performing AI on the client with true end-to-end encryption is not optional, it is the only responsible architecture. Cloud-based AI inherently creates a vector for data exfiltration, whether through subpoenas, breaches, or insider threats. Client-side processing keeps plaintext data within the organization’s security perimeter at all times.
End-to-end encryption ensures that even the AI model itself cannot be compelled to reveal content. This approach directly addresses the “sovereignty crisis” described in forward-looking analyses: centralized cloud architectures force organizations to surrender control of their most sensitive assets. By contrast, JACE 3 delivers powerful intelligence while preserving absolute confidentiality; critical for national security agencies handling classified information, healthcare providers protecting patient privacy rights, and financial institutions safeguarding client and competitive data.
Industry experts agree. As Grokipedia documents [13], the importance of private AI deployments and data sovereignty intensifies in 2026 precisely because organizations seek to mitigate risks associated with public cloud dependencies and regulatory requirements. Client-side encryption, confidential computing, and customer-managed keys have become baseline expectations in high-security and regulated industries.
Early adopters of JACE 3 report dramatic outcomes:
JACE Version 3 is available immediately for on-premises, air-gapped, and hybrid sovereign deployments. The SDK supports common programming languages and includes comprehensive documentation, reference implementations, and enterprise support packages.
MailSPEC delivers AI governance and compliance technology for communication channels, trusted by the world’s most security conscious and regulated organizations. With a relentless focus on sovereignty, data privacy, and regulatory excellence, MailSPEC empowers enterprises and public service agencies to innovate confidently in an increasingly complex regulatory landscape.
For more information, visit www.mailspec.com
Sarah Linden
Director of Investor relations and public communications, MailSPEC
+1 (415) 569-2280
1. Grokipedia. (2026). 2026 in Information Technology. Retrieved March 14, 2026, from https://grokipedia.com/page/2026_in_information_technology
Deloitte. (2025). Technology, Media & Telecommunications Predictions 2026: A new era of self-reliance – Navigating technology sovereignty. Deloitte Insights. https://www.deloitte.com/us/en/insights/industry/technology/technology-media-and-telecom-predictions/2026/tech-sovereignty.html
Deloitte Global. (2025). Deloitte 2026 Technology, Media & Telecommunications Predictions. Press release, November 2025. https://www.deloitte.com/global/en/about/press-room/2026-tmt-predictions.html
2. EU AI Act text (eur-lex.europa.eu), Article 99.
3. (2023). Regulation (EU) 2023/2854 of the European Parliament and of the Council of 13 December 2023 on harmonised rules on fair access to and use of data (Data Act). Official Journal of the European Union. https://eur-lex.europa.eu/eli/reg/2023/2854/oj
4. Gaia-X European Association for Data and Cloud AISBL. (n.d.). Gaia-X: A Federated Secure Data Infrastructure. Official website. https://gaia-x.eu/
5. Gartner, Inc. (2025, November 12). Gartner Survey Reveals Geopolitics Will Drive 61% of CIOs and IT Leaders in Western Europe to Increase Reliance on Local Cloud Providers. Press release. https://www.gartner.com/en/newsroom/press-releases/2025-11-12-gartner-survey-reveals-geopolitics-will-drive-61-percent-of-cios-and-information-technology-leaders-in-western-europe-to-increase-reliance-on-local-cloud-providers
6. PwC. (2026, January 6). Five GCC economic themes to watch in 2026. PwC Middle East. https://www.pwc.com/m1/en/blog/five-economic-themes-to-watch-2026-gcc.html
7. https://www.japaneselawtranslation.go.jp/en/laws/view/4241/en
8. EURAXESS (European Commission). EU-Japan Digital Week events listing: https://euraxess.ec.europa.eu/worldwide/japan/events/eu-japan-digital-week-2025 (for the 2025 edition, with similar framing).
9. Factsheet on the Japan-EU Digital Partnership (from the launch in 2022): https://digital-strategy.ec.europa.eu/en/library/japan-eu-digital-partnership-factsheet
Joint Statement of the Third Meeting of the EU-Japan Digital Partnership Council (May 12, 2025): https://digital-strategy.ec.europa.eu/en/library/joint-statement-third-meeting-european-union-japan-digital-partnership-council
10. National Cybersecurity Office (NCO), Cabinet Secretariat, Japan. (2025, December 23). Outline of the Cybersecurity Strategy (Tentative English translation). https://www.cyber.go.jp/pdf/policy/kihon-s/cs_strategy2025_abstract_english.pdf
Cabinet Secretariat, Japan. (2025, December 23). サイバーセキュリティ戦略 [Cybersecurity Strategy]. https://www.cyber.go.jp/pdf/policy/kihon-s/cs_strategy2025.pdf
House of Representatives, National Diet of Japan. (2025). Bill on the Development of Active Cyber Defense (Enacted May 16, 2025). https://www.shugiin.go.jp/internet/itdb_gian.nsf/html/gian/honbun/houan/g21306007.htm
Cabinet Secretariat, Japan. (2025). サイバー安全保障に関する取組(能動的サイバー防御の実現に向けた検討など). https://www.cas.go.jp/jp/seisaku/cyber_anzen_hosyo_torikumi/index.html
Baker McKenzie – Connect On Tech. (2026, January 22). Japan’s New Active Cyber Defense Law: Impact on Businesses. https://connectontech.bakermckenzie.com/japans-new-active-cyber-defense-law-impact-on-businesses
11. Personal Information Protection Commission (PPC), Japan. (2026, January 9). System Reform Policy under the Triennial Review of the Act on the Protection of Personal Information Has Been Decided (January 9, 2026). https://www.ppc.go.jp/en/topix/triennial_review_2026_02/
12. Fujitsu Limited. (2026, February 12). Fujitsu Group starts manufacturing sovereign AI servers in Japan to enhance digital sovereignty. Fujitsu Global. https://global.fujitsu/en-global/pr/news/2026/02/12-01
13. Grokipedia. (2026). 2026 in Information Technology. Retrieved [current date, e.g., March 14, 2026], from https://grokipedia.com/page/2026_in_information_technology
MailSPEC, a leader in compliance technology for communications, today announced the launch of PassLink 2.0, an innovative encrypted file-sharing tool designed to protect the sovereign integrity of sensitive data. In an era where data breaches and unauthorized surveillance pose constant threats, PassLink empowers organizations to share files securely without compromising jurisdictional control or exposing information to external risks.
PassLink addresses a critical challenge, especially so for Regulated Industries that are restricted from transporting sensitive data beyond national borders or jurisdictional boundaries. By enabling the creation of encrypted links for file access, it ensures that proprietary or confidential information remains under the sender's control, even when transmitted through potentially vulnerable channels. Recipients authenticate with their existing identity (Microsoft, Google, or OTP). This is particularly vital for sectors such as defense, finance, and government, where regulations prohibit data from leaving territorial confines to prevent espionage, compliance violations, or loss of sovereignty.
In healthcare, for instance, PassLink allows providers to securely share patient records, medical images, or treatment plans directly with individuals. Files can be shared via everyday email services such as Yahoo, Gmail, or Office 365; platforms hosted on global cloud systems that often scan content for user profiling, advertising, or other nefarious purposes. With PassLink, files are strongly encrypted end-to-end, rendering them inaccessible to intermediaries or unauthorized parties. The services are self-hosted, placed in a private cloud, national cloud, or on-premises of the enterprise. This means healthcare professionals can maintain patient privacy and comply with data sovereignty requirements, all while using familiar, convenient communication tools without the need for outsourcing to vulnerable shared infrastructure.
"PassLink is a game-changer for organizations navigating stringent data
protection laws”, said Tanguy Godquin - PhD, Research & Development director at MailSPEC. "It eliminates the burdens of traditional secure file transfer methods, offering seamless integration that meets policy requirements without added complexity."
Key to PassLink's appeal is its robust compliance framework. The solution supports adherence to major international regulations, including Japan's Act on the Protection of Personal Information (APPI), Europe's Markets in Financial Instruments Directive II (MiFID II), and the U.S. Securities and Exchange Commission's Rule 17a-4. Businesses can remain compliant with these policies, ensuring data retention, auditability, and privacy, while avoiding operational hurdles, such as restricted workflows.
PassLink's features include:
Available now, PassLink is poised to transform how Regulated Industries handle file sharing. For more information or to schedule a demo, visit
MailSPEC specializes in compliance technology for communications that prioritize data privacy and sovereignty. With a focus on innovation, the company serves clients across healthcare, finance, and government sectors worldwide.
The healthcare industry is undergoing a massive digital transformation. Telehealth, electronic health records (EHRs), and remote patient monitoring have revolutionized patient care. But with these advancements comes a serious challenge—keeping patient data secure.
Cyber threats targeting healthcare organizations are at an all-time high, with data breaches leading to financial loss, legal consequences, and—most importantly—compromised patient trust. That’s why secure communication for healthcare professionals isn’t just a best practice; it’s a necessity.
At MailSPEC, we understand the unique security challenges healthcare professionals face. Our solutions offer HIPAA-compliant communication tools, secure messaging, and encryption technologies that ensure medical teams can collaborate without compromising patient privacy.
Healthcare organizations have embraced technology to improve efficiency, patient outcomes, and collaboration. However, this digital shift has also increased the risks of data breaches, ransomware attacks, and unauthorized access to sensitive patient information.
Does this sound familiar? If so, you’re not alone.
Despite the strict requirements of regulations like HIPAA (Health Insurance Portability and Accountability Act) to protect electronic health information (ePHI), too many healthcare organizations still rely on outdated or insecure communication tools. These tools not only put patient data at risk but could also lead to costly compliance violations.
So, what’s the solution? Updating your communication systems to be secure, user-friendly, and made specifically for healthcare is a great place to start. It’s time to leave behind risky practices and step into a safer, smarter future for healthcare communication.
Let’s face it: traditional communication methods like unencrypted email or text message (or SMS) just don’t cut it anymore. They leave sensitive patient data vulnerable to hackers and breaches. As a healthcare provider, keeping your patients’ information safe isn't just a priority—it’s a responsibility.
And that is where secure messaging for healthcare professionals comes in. By using encryption, you can send messages with confidence, knowing they’ll stay private.
MailSPEC’s EasyCrypt technology makes email encryption seamless and hassle-free, so you can communicate securely without adding extra steps to your busy workflow. It is security you can count on—without slowing you down.
Sharing patient records, test results, and treatment plans is an integral part of providing quality care. But did you know that using consumer-grade file-sharing apps can put that information at risk? And when it comes to healthcare, secure file sharing isn’t just a “nice-to-have”—it’s a must-have.
MailSPEC’s Réunion platform gives you everything you need to share files safely, including:
With Réunion, your team can collaborate easily while keeping patient data fully protected. It’s peace of mind for both you and your patients.
HIPAA compliance is no joke. Following the Health Insurance Portability and Accountability Act rules is very important. We’ve all heard the horror stories of organizations facing hefty fines and lawsuits for failing to meet the required standards for protecting patient information. So, how do you make sure your communication tools are up to the task?
MailSPEC’s HIPAA-compliant communication tools are designed to keep you on the right side of the law while making your job easier. With features like:
You can focus on what you do best—caring for your patients—without worrying about compliance risks.
Telehealth has revolutionized the way healthcare professionals connect with patients. But let’s be honest: using generic video conferencing apps for virtual consultations is risky. They lack the security features needed to protect sensitive conversations.
MailSPEC’s Réunion platform is built for secure collaboration for medical teams, offering:
Whether you’re checking in with patients remotely or hosting team meetings, you can trust Réunion to keep your conversations secure.
Remote patient monitoring (RPM) is a game-changer for tracking patients outside the clinic, but it comes with its own set of security challenges. Sharing RPM data must be done securely to protect patient privacy and comply with regulations.
MailSPEC’s CommuniGate SPEC platform ensures that RPM data, alerts, and updates are shared securely within your team. It’s designed to keep communication smooth, efficient, and fully compliant, so you can focus on delivering the best care possible.
Did you know that healthcare organizations are one of the top targets for cybercriminals? From phishing scams to ransomware attacks, the risks are real—and the consequences can be devastating.
MailSPEC’s MailToken technology is here to help. By adding biometric authentication to critical email communications, it offers an extra layer of protection against phishing attacks and credential theft.
It’s like having a digital shield for your emails, ensuring that sensitive information stays out of the wrong hands.
It’s not just healthcare providers who need secure communication—administrators play a crucial role in protecting sensitive information related to insurance, billing, and patient records. Using insecure communication channels can put that data at risk.
MailSPEC’s ActiveAuth technology ensures that only the right people have access to sensitive information. And with features like multi-factor authentication and robust account protection, you can rest easy knowing your administrative operations are secure.
At the end of the day, secure communication isn’t just about ticking boxes—it’s about building trust. When your patients know their information is safe, they can focus on their care. And when your team has the right tools, they can work more efficiently and confidently.
With MailSPEC, healthcare organizations benefit from:
✔️ Encrypted messaging for patient confidentiality
✔️ HIPAA-compliant communication tools for secure telehealth and collaboration
✔️ Secure file sharing for medical professionals
✔️ Multi-factor authentication to prevent unauthorized access
✔️ Phishing protection to safeguard against cyber threats
MailSPEC provides a complete suite of secure communication tools tailored for healthcare professionals. Our solutions enable medical teams to collaborate effectively while maintaining compliance with HIPAA and other regulations.
Healthcare professionals cannot afford to take risks when it comes to patient data security. Whether you are running a hospital, a private practice, or a telehealth service, secure communication for healthcare professionals is non-negotiable.
Ready to upgrade your healthcare communication security? Contact MailSPEC today and take the first step toward safer, compliant, and more efficient collaboration.
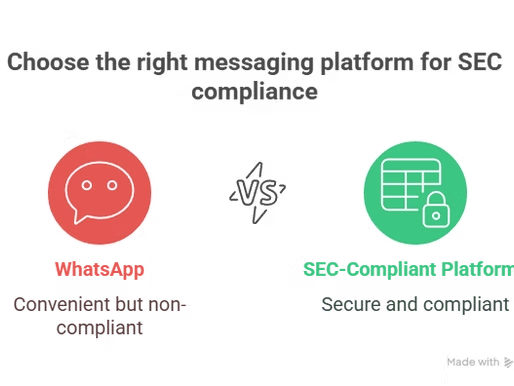
While WhatsApp is convenient and widely used, it simply doesn’t meet the rigorous standards required by regulatory bodies like the SEC (Securities and Exchange Commission). This seemingly helpful app could end up exposing your business to unnecessary compliance risks.
Thankfully, there are messaging platforms specifically designed to handle the complexities of regulated industries. These solutions not only meet but often exceed the SEC’s requirements for secure and compliant communication tools.
At MailSPEC, we specialize in helping organizations switch seamlessly to SEC-compliant messaging solutions that address both security needs and business workflows.
Keep reading to learn five compelling reasons why your business needs a WhatsApp alternative for SEC compliance.
Let’s be honest—WhatsApp is great for chatting with friends. But for industries like finance, healthcare, or legal services, it’s not the right tool. These sectors have strict rules to follow, and using WhatsApp for sensitive business communication brings hefty compliance risks.
The good news? You don’t have to stick with consumer apps that don’t meet your needs. Switching to an enterprise messaging platform designed for compliance removes the guesswork.
Tools like MailSPEC offer encrypted communication, detailed logs, and features tailored to meet the demands of industries like yours. The result? Your business stays compliant with far less stress.
While WhatsApp may promise end-to-end encryption, that’s not enough to meet the broader security requirements of regulated industries. Security breaches can happen more easily on platforms like WhatsApp, which weren’t designed with enterprise needs in mind.
Replacing WhatsApp with a secure, SEC-compliant messaging solution like MailSPEC means you can confidently protect your data. These tools provide enterprise-grade encryption, role-based access control, and system-wide oversight to ensure every message stays secure at every step.
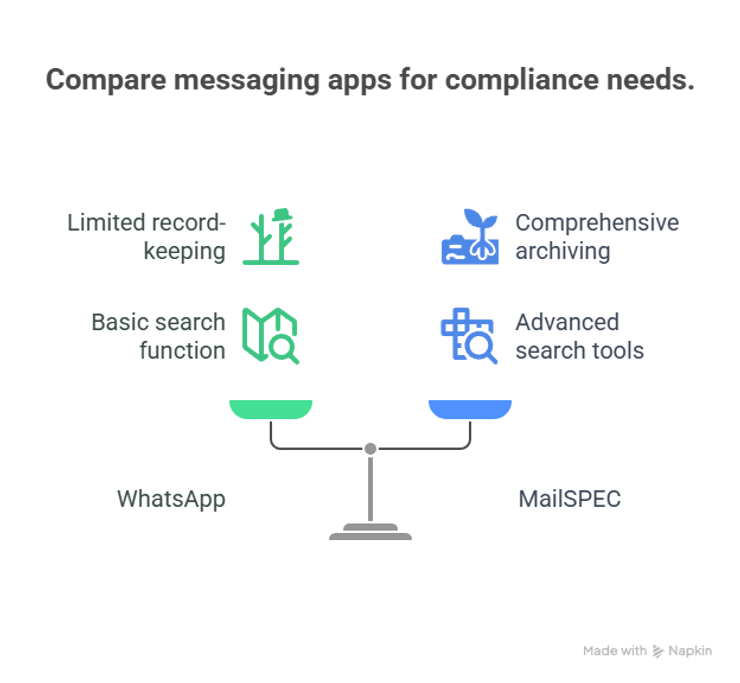
Keeping detailed records is a must for messaging apps for regulated industries, especially when it comes to audits or legal compliance. Unfortunately, WhatsApp doesn’t make record-keeping easy—or even possible in some cases.
An SEC-compliant messaging app like MailSPEC does the heavy lifting for you. Messages are automatically archived and stored securely, making them tamper-proof and easy to retrieve during audits. Plus, you’ll save time with built-in search tools that simplify the process of finding specific interactions.
Every business is unique, and enterprise messaging compliance requirements can vary across industries. Unfortunately, WhatsApp’s “one-size-fits-all” design doesn’t allow for the customization businesses need to meet specific regulatory demands.
Switching to a customizable messaging platform like MailSPEC gives you full control over your communication channels. From user permissions to compliance monitoring, these tools are tailored to meet your specific regulatory needs, ensuring you stay in control and on top of compliance.
Compliance isn’t just about avoiding fines—it’s about showing clients, stakeholders, and regulators that you take data security and transparency seriously. Using non-compliant tools like WhatsApp can quickly damage your reputation.
By adopting an SEC-compliant messaging solution, you’re not just protecting your data—you’re showing clients and regulators that you value integrity and professionalism. Tools like MailSPEC help you safeguard your reputation while staying one step ahead of compliance requirements.
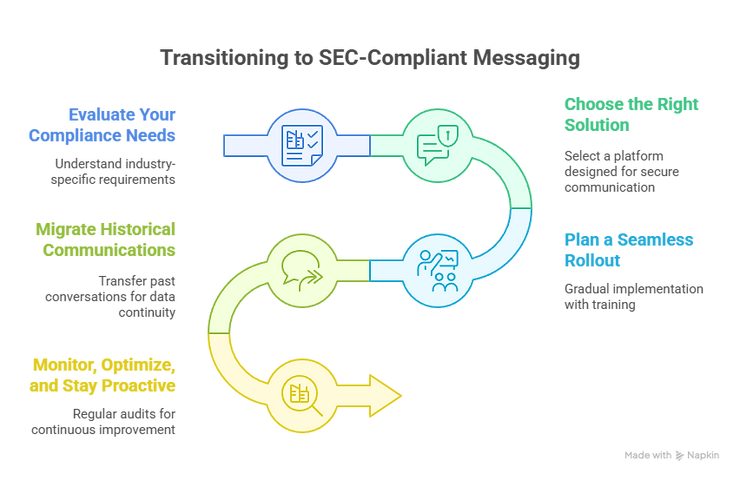
By now, you’ve probably realized why switching to a WhatsApp alternative for SEC compliance is so important. But how do you actually go about making the shift?
Migrating your team to a secure messaging for SEC compliance platform doesn’t have to be complicated. Let’s break it down with this simple roadmap.
Start by understanding your industry’s specific compliance requirements. Are there strict data retention rules? Do you need detailed audit trails or custom governance settings? Identifying these needs upfront will help you choose the right platform that fits like a glove.
Look for a messaging platform designed specifically for secure communication in regulated industries—something built with features like end-to-end encryption, detailed reporting, and tailored governance options.
Tools like MailSPEC are made to meet SEC compliance requirements while ensuring your team’s workflow isn’t disrupted.
Don’t just spring the change on your team overnight. Plan a gradual rollout of the new system. Pair it with clear communication, step-by-step guides, and training sessions to get everyone up to speed. Change can be tricky, but with proper guidance, your team will adapt in no time.
If possible, transfer important past conversations from WhatsApp to your new platform. This ensures that you maintain data continuity and avoid any compliance gaps. Plus, having those records in one place will save you headaches down the line.
The work doesn’t stop after implementation. Regular compliance audits are your best friend—use them to evaluate how the new system is performing and identify any areas for improvement. Staying proactive means staying ahead of potential WhatsApp for business compliance issues.
We specialize in developing messaging tools for regulated industries that simplify compliance without adding extra stress. Our platform offers a perfect mix of robust security, seamless onboarding, and the flexibility your team needs to thrive.
Whether you’re navigating SEC compliance or other industry regulations, MailSPEC is here to support you every step of the way.
Ready to make the switch with confidence?
Don’t leave your business exposed to WhatsApp compliance risks. With regulations becoming more demanding, now is the time to adopt a secure, enterprise-level solution.
MailSPEC is here to help. Our robust messaging tools are designed from the ground up to ensure your business meets SEC communication standards while streamlining operations.
➡️ Learn more about our SEC-compliant messaging solutions.
➡️ Schedule a demo with our team and see how easy it is to migrate.
Your business deserves better—and so do your clients. It’s time to ditch WhatsApp and invest in a messaging platform that protects your data, your clients, and your organization’s future.
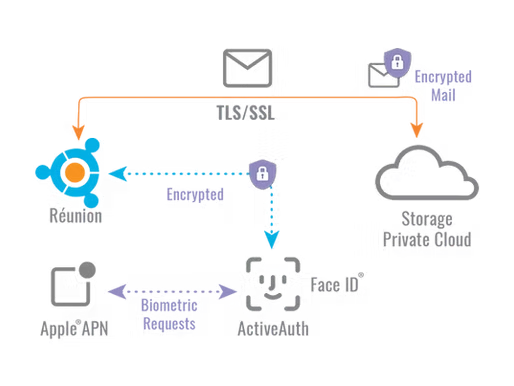
In today’s fast-paced, hyper-connected world, the way employees communicate has shifted dramatically. Gone are those days of clunky desktop software and delayed email chains. The workforce — especially younger employees — now expects mobile-first experiences that mirror the convenience of consumer messaging apps.
But when you are operating in these regulated industries, ease of use cannot come at the cost of compliance. So how can enterprises deliver user-friendly secure messaging without compromising on data security and regulatory standards?
Well, that’s where MailSPEC comes in.
As your trusted partner in regulatory solutions, MailSPEC builds secure mobile communication platforms that prioritize both security and usability. Below, we break down these eight essential principles for designing mobile-first secure messaging platforms that meet user expectations and enterprise compliance needs.
Millennials and Gen Z now make up a large percentage of the workforce. And these employees are digital natives, accustomed to real-time, app-based communication. And even in highly regulated industries like finance, healthcare, and legal, they expect:
Now, ignoring this shift creates friction that actually slows down workflows and even encourages shadow IT — the unauthorized use of apps like WhatsApp or Telegram for business communication.
The solution? Build a secure messaging platform design that aligns with mobile-first behavior while staying within regulatory boundaries.
Smartphones and tablets introduce a unique set of risks, which secure messaging platforms must address from day one:
MailSPEC’s mobile-first communication security approach ensures robust controls such as remote wipe capabilities, secure sandbox environments, and identity-based access protocols tailored for mobile.
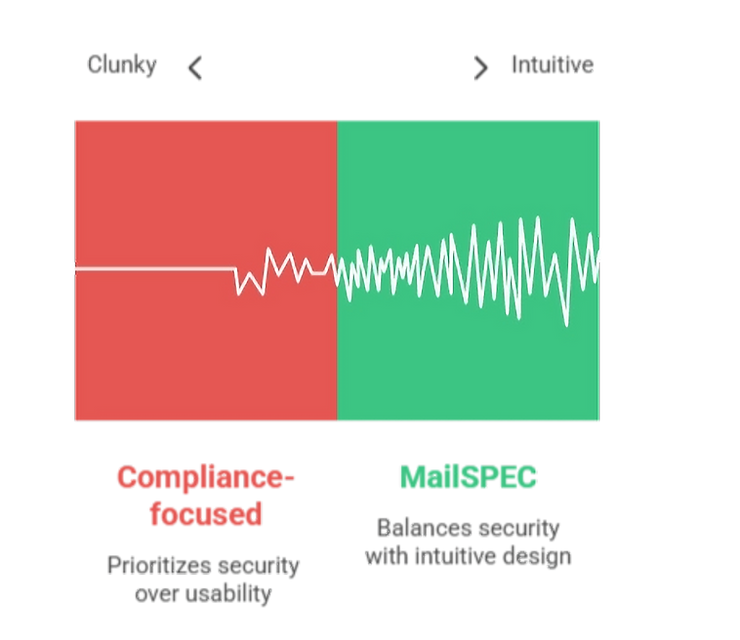
Compliance and cybersecurity cannot be an excuse for clunky software. A good mobile-first secure messaging platform is one that employees want to use.
Key UX principles include:
By following these same principles, MailSPEC ensures user-friendly, secure messaging that balances enterprise-grade protection with intuitive experiences.
Too often, compliance is bolted onto an app after the fact. Well, that never works long-term.
Instead, compliance in mobile messaging must be a foundational element. This means:
MailSPEC's secure mobile communication tools are also built with these features at the core, ensuring your organization remains audit-ready at every step.
Users should never have to think about whether their messages are secure. The best platforms embed these strong protections behind the scenes without actually disrupting the user journey.
For example, MailSPEC:
This "secure-by-default" approach makes mobile-first secure messaging truly seamless for the user, yet uncompromising for the enterprise.
It is no surprise that employees default to apps like WhatsApp, iMessage, or Signal when company tools are too rigid. Now the key here is not to fight that impulse, but to meet it with better tools.
MailSPEC mimics the features users love:
... while enforcing enterprise-grade protections in the background. It is the best of both worlds: mobile secure messaging apps that users enjoy, and security teams can trust.
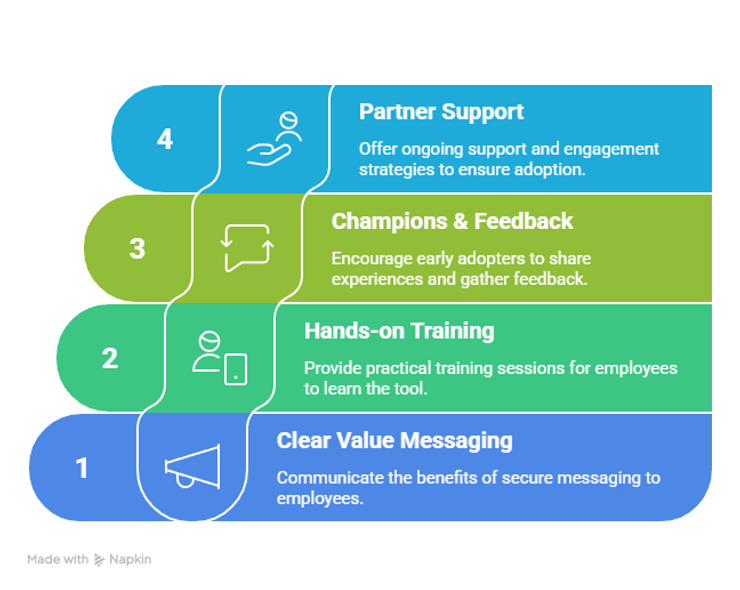
Secure messaging tools only work if employees use them. So that means organizations need an adoption plan that includes:
With MailSPEC, clients get more than just a tool — they get a partner. Our team supports onboarding, change management, and as well as custom user engagement strategies.
Technology evolves fast, and mobile-first secure messaging platforms must keep up. That means building on a flexible architecture that can also adapt to new regulations, devices, and integrations.
MailSPEC’s secure messaging platform design supports:
And as communication norms change, your secure mobile communication infrastructure should evolve with them — not get left behind.
Balancing user-friendly, secure messaging with compliance in mobile messaging does not have to be a losing battle. In fact, with the right design principles and the right partner, it becomes a solid competitive advantage.
MailSPEC delivers mobile-first secure messaging solutions that:
So whether you are securing communication in healthcare, finance, legal, or any other regulated sector, the future is mobile-first. And with MailSPEC, it is also secure-first.
Ready to give your team the tools they want and the protection your enterprise needs?
Contact MailSPEC today to schedule a personalized demo and discover how our mobile-first secure messaging solutions can transform the way your business communicates—safely, compliantly, and confidently.
Executives now chat, message, and collaborate across dozens of platforms, often from mobile devices. While this flexibility boosts productivity, it also introduces a significant challenge: ensuring those communications stay compliant with regulations.
Welcome to the new frontier of compliance—and artificial intelligence is at the center of it.
For C-level leaders navigating risk, security, and compliance, understanding the strategic role of Artificial Intelligence for Compliant Messaging isn’t optional anymore—it’s a business necessity. And at MailSPEC, we’re here to help you unlock that advantage without overwhelming your teams with complexity.
Before we dig into the impact of artificial intelligence, it’s crucial to understand the compliance pain points that organizations face.
Employees increasingly turn to unapproved platforms (like personal messaging apps) for convenience, opening organizations up to “off-channel” risk—a compliance nightmare, especially for regulated industries like finance and healthcare.
Many businesses allow employees to use personal devices for work, a practice known as BYOD. While convenient for users, this significantly complicates data security and compliance monitoring efforts.
Today’s regulatory frameworks place extensive demands on businesses to ensure compliant communication practices. Failing to meet these requirements can result in serious penalties.
Now, think about adding AI into the mix.
With artificial intelligence for compliant messaging, businesses can efficiently address these challenges while simultaneously enabling smarter communication workflows.
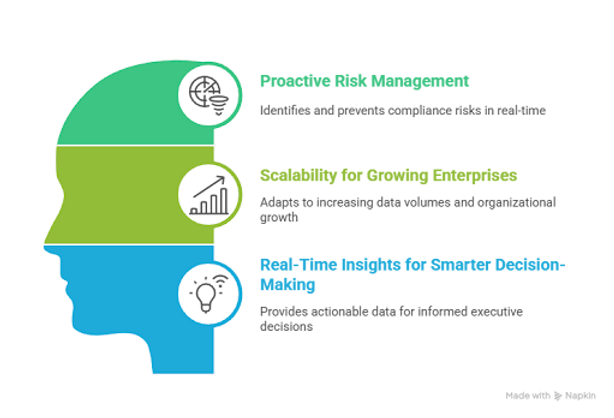
Why should executives care about integrating artificial intelligence into communication compliance?
Here’s what sets AI apart as a game-changer for future-ready organizations:
Most traditional compliance systems only step in after mistakes have already happened. That’s where they fall short. Imagine having a system that not only identifies errors but prevents them from happening in the first place. Sounds good, right?
AI tools can analyze communication data across multiple channels in real time, flagging high-risk activities before they escalate into full-blown problems.
And for instance, AI-powered algorithms can detect when sensitive documents are being shared without approval or when employees are using off-channel communication platforms—addressing potential compliance violations before they even occur.
Managing compliance at scale can be a daunting task, especially for enterprises dealing with massive amounts of communication traffic. The good news? AI thrives on data.
It seamlessly scales with your organization, ensuring that all interactions—no matter how many—are monitored effectively. Whether you’re a growing startup or a large enterprise, it adapts to your workflow and ensures your compliance infrastructure grows alongside you.
No more worrying about missing something important in the flood of daily communications. AI’s scalable algorithms have you covered.
Here’s the thing—AI doesn’t just help you stay compliant; it helps you lead smarter.
By analyzing communication trends and identifying risky behaviors, it delivers insights that empower executives to take action. Want to know where your organization is most vulnerable? AI can pinpoint the patterns and help you strengthen your risk strategies.
These insights aren’t just technical details—they’re actionable, real-time data that give you a clear picture of what’s happening and where improvements can be made.
And here at MailSPEC, we take pride in offering AI-powered compliance solutions that not only spot risks but also provide meaningful insights tailored for the C-suite. This means you get more than just an automated tool—you get an intelligent ally in decision-making.
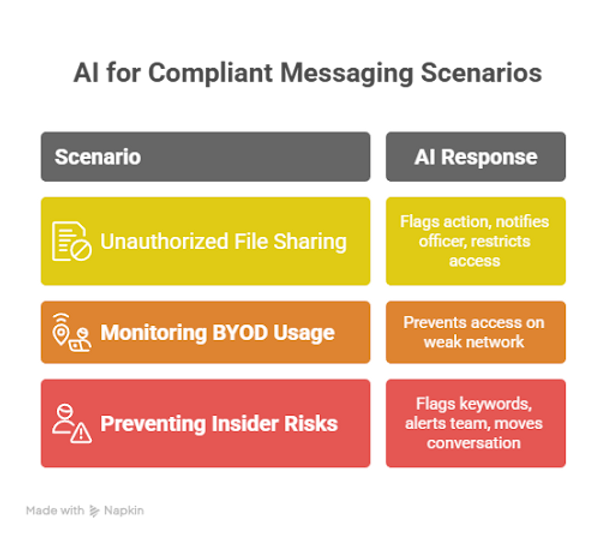
Curious about how AI impacts compliance?
These real-world scenarios illustrate the power of AI for compliant messaging in action:
Scenario: A financial analyst shares a sensitive report using an unapproved personal messaging app.
AI Response: An AI-powered monitoring system detects the file-sharing attempt. It flags the action, notifies the compliance officer, and restricts further dissemination of the document—all in real time.
Scenario: A team member logs into secure messaging on a personal tablet while connected to public Wi-Fi.
AI Response: AI recognizes the weak security context of the connection and prevents access automatically, requiring the employee to switch back to an approved network before proceeding.
Scenario: An employee drafts replies to an off-channel email thread that discusses merger negotiations.
AI Response: AI instantly flags keywords indicating sensitive topics, alerts the compliance team, and ensures the conversation moves to an approved and encrypted platform.
These scenarios demonstrate why MailSPEC’s platform is a trusted solution for artificial intelligence in enterprise compliance. From blocking risky behavior to empowering compliance teams with instant alerts, we take the complexity out of communication safety.
Now, if you’re evaluating solutions, here’s your checklist:
✅ Inline message scanning
✅ Policy-driven content filtering
✅ Integration with your existing platforms (e.g., Microsoft 365)
✅ Automated audit trails
✅ Localization and sovereignty support
✅ Real-time risk scoring and alerts
These features aren’t future luxuries—they’re current necessities.
Investing in AI-powered compliance tools might seem like a significant upfront cost, but it’s one with a measurable return on investment.
Regulatory fines don’t just chip away at your bottom line—they impact your reputation and prevent you from meeting operational goals. With AI reducing compliance errors, businesses can save millions in potential fines and legal fees.
AI handles repetitive risk management tasks, freeing up your compliance team to focus on value-driven initiatives. This increases productivity across the board while ensuring airtight systems for secure enterprise messaging AI.
With audit-ready logs and transparent oversight, AI tools streamline regulatory reviews—cutting down time and costs during investigations.
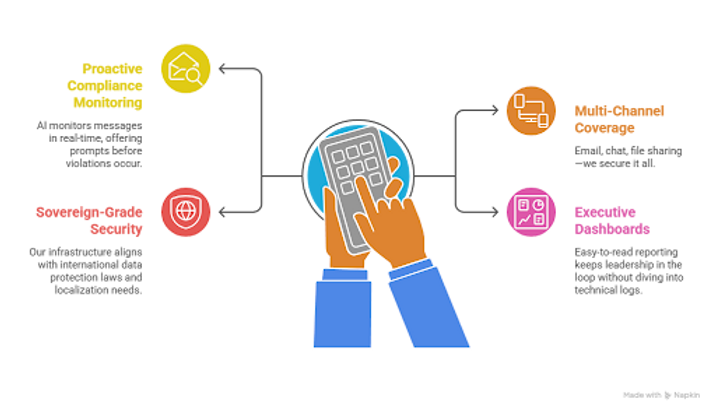
We’re not about throwing complicated tech at your teams. We focus on regulations-first solutions that are simple to use and powerful under the hood.
✔️ Proactive Compliance Monitoring: AI watches messages in real-time, offering prompts before violations occur.
✔️ Multi-Channel Coverage: Email, chat, file sharing—we secure it all.
✔️ Sovereign-Grade Security: Our infrastructure aligns with international data protection laws and localization needs.
✔️ Executive Dashboards: Easy-to-read reporting keeps leadership in the loop without diving into technical logs.
We believe compliant communication for executives should feel effortless—not a burden.
Regulators aren’t slowing down. In fact, rules are tightening across industries and borders. The only way to stay ahead is to embed smart, automated compliance into your operations.
AI makes that possible.
It removes human error, offers real-time guidance, and provides a buffer between your communications and legal risk. And for the executive team, that means fewer headaches, fewer lawsuits, and a much stronger risk posture.
Whether you’re in government, healthcare, or enterprise, MailSPEC helps you:
→ Stop risky messages before they’re sent
→ Gain full visibility into off-channel communication
→ Empower your teams with secure, compliant tools that feel natural to use
Ready to unlock smart, AI-backed compliance?
Contact MailSPEC for a personalized demo and C-level strategy session.
Whether you are in healthcare, finance, legal, or any regulated industry, staying ahead of these ever-changing rules isn't just about avoiding fines. It is about preserving the trust, protecting data, and maintaining operational resilience.
But let’s be honest: manual compliance processes are time-consuming, error-prone, and downright exhausting. But that’s where automated compliance workflows come in.
At MailSPEC, we understand that enterprise messaging compliance can feel like chasing a moving target. Our mission here is to simplify that chase. This guide walks you through ten practical steps to implement automation that keeps you compliant, reduces risk, and frees up your IT team to focus on what they do best.
Before you automate anything, you need to know what you are automating for. Compliance standards vary by industry and geography:
Knowing which regulations apply to your organization is the foundation of smart automation.
Now, from email and instant messaging to file sharing and mobile apps—you need a full picture of how your teams communicate.
Automation starts with visibility. Without it, you’re flying blind.
Automation is only as good as the rules it follows. So, you should better work with compliance officers and legal teams to define:
These become the blueprint for your automated compliance solutions.
One of the major benefits of compliance workflow automation is catching violations before they even become liabilities.
MailSPEC enables real-time policy enforcement, such as:
✔️ Blocking unapproved file transfers
✔️ Flagging use of personal messaging apps for work
✔️ Enforcing retention rules for chat messages and emails
This proactive approach keeps your organization on the right side of compliance.
The best systems don’t just monitor—they act!
MailSPEC automatically detects:
Plus, automated alerts go straight to your compliance team, reducing detection time and improving incident response.
Catching violations is your step one. Then, fixing them is just as important, too!
MailSPEC lets you automate steps like:
Secure enterprise messaging isn’t just about prevention here. It’s about a smart, efficient response.
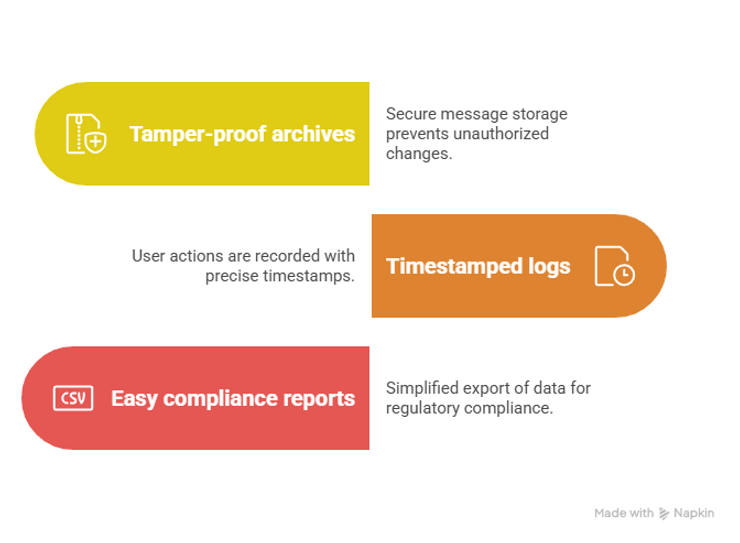
If regulators come knocking, will you be ready?
Manual logs are messy and unreliable. But, automated systems give you:
✔️ Tamper-proof message archives
✔️ Timestamped logs of user actions
✔️ Easy-to-export compliance reports
MailSPEC makes sure your compliance records are always audit-ready.
Automation is powerful—but it’s clearly not infallible. Compliance still needs a human touch.
Our platform empowers teams to step in when nuance is required, while automation handles the heavy lifting.
Let's talk numbers here.
Companies using automated compliance workflows save on:
And according to MailSPEC data:
Organizations can reduce compliance-related administrative workload by up to 60%, while cutting response times by more than half.
So when you automate smartly, compliance becomes an asset—not just a cost center.
Not all automation tools are created equal.
MailSPEC offers:
✔️ Industry-specific compliance automation (HIPAA, GDPR, SEC, SOX)
✔️ Customizable rulesets tailored to your risk profile
✔️ Secure enterprise messaging with end-to-end encryption
✔️ Scalable deployment across cloud, on-premise, and hybrid environments
And most importantly, we focus on regulatory solutions first—not just software.
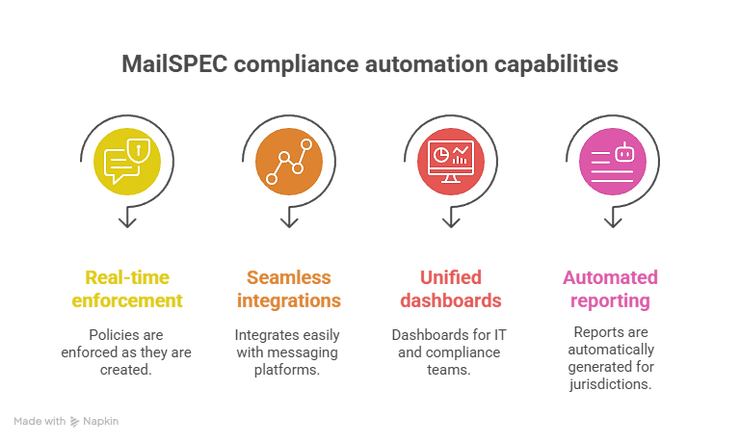
Well, when it comes to enterprise compliance workflows, most platforms bolt on security as an afterthought. Here at MailSPEC, it is built into our DNA.
Our compliance automation capabilities include:
✔️ Real-time policy enforcement
✔️ Seamless integrations with enterprise messaging platforms
✔️ Unified dashboards for IT and compliance teams
✔️ Automated reporting for multiple jurisdictions
All designed to make your job easier, your data safer, and your workflows even smoother.
We get it—compliance can sure feel overwhelming. But with the right tools, the right workflows, and the right partner, you can turn complexity into clarity.
Automated compliance workflows don’t just protect your business. They empower it. So the question isn’t whether you can afford to implement automation.
The real question is: can you afford NOT to?
Let’s talk about what automated compliance looks like for your organization.
Contact us today to schedule a demo or consultation with our compliance specialists.
In today’s global business environment, enterprise messaging is not just about efficiency — it’s now all about compliance, too!
For multinational organizations, staying on the right side of communication laws is not as simple as checking a single box. Different countries and regions have their ideas of what “compliant messaging” looks like.
And navigating these overlapping regulations? It sure can feel like walking a tightrope over international red tape.
But that’s where MailSPEC comes in. We help enterprises like yours simplify the complex, enabling secure, compliant communication across borders without sacrificing usability, speed, or consistency.
In this guide, we will walk you through the challenges of multi-jurisdictional compliance for enterprise messaging and offer practical insights on how to build systems and policies that withstand scrutiny across multiple regulatory environments.
Before we dive into country-by-country specifics, let’s break down what we mean by multi-jurisdictional compliance for enterprise messaging.
In simple terms, it refers to the need for organizations to follow communication and data security laws across every jurisdiction where they operate — and to do so simultaneously.
That includes:
Now, with the rise of remote work, global teams, and cloud-based tools, enterprise messaging is under more scrutiny than ever. What’s considered secure or legal in one country might be restricted or illegal in another.
So how do you keep everyone connected, protected, and compliant — from New York to Tokyo to Berlin? Well, let’s start by looking at what the major global markets expect.
In the U.S., enterprise communication regulations often hinge on industry.
Financial firms, for instance, fall under Financial Industry Regulatory Authority (FINRA) and Securities Exchange Commission (SEC) rules that require retention of all business-related messages — including instant messaging and texts. Healthcare organizations must comply with the Health Insurance Portability and Accountability Act of 1996 (HIPAA), which mandates encryption and secure access.
And there is also a growing crackdown on shadow IT. The SEC has recently issued multimillion-dollar fines to companies for failing to monitor off-channel communications like WhatsApp.
The EU’s General Data Protection Regulation (GDPR) is one of the most influential privacy laws in the world. It also places tight limits on how personal data is collected, stored, and transferred too including through enterprise messaging tools.
And note that penalties for GDPR violations can be up to 4% of global annual revenue. The emphasis in the EU is less on retention and more on individual rights, transparency, and data minimization.
Now, unlike the U.S. or EU, the Asia-Pacific region is not governed by a single framework. Countries like China, Singapore, Japan, and Australia all have unique — and often strict — rules on data handling and enterprise communication.
Note that in many Asian countries, language, culture, and enforcement styles also vary, adding another layer of complexity for global enterprises.
Here is where things get particularly tricky: many jurisdictions now require data localization — meaning certain types of data must be stored within national borders. Yes, and that is a problem for cloud-based or multinational messaging platforms that rely on distributed systems.
Countries like China, Russia, India, and Brazil have implemented these strict data localization laws, which can somehow conflict with the need for centralized data management.
Similarly, cross-border messaging compliance requires enterprises to carefully control where message data travels, who has access to it, and as well as how it’s encrypted or anonymized in transit.
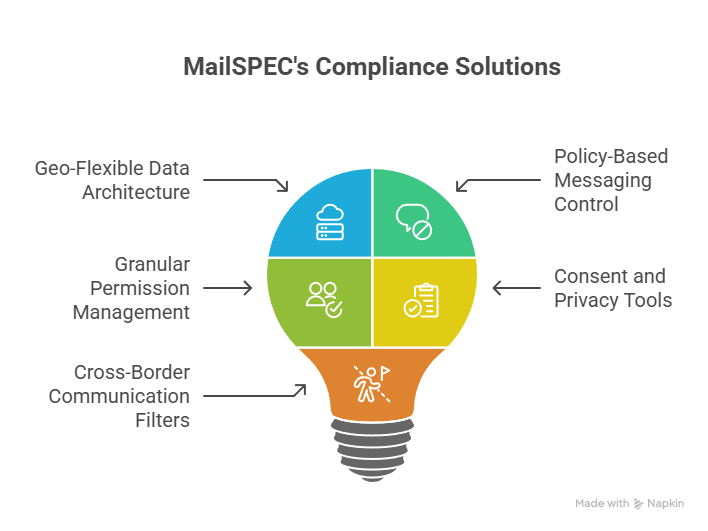
Now, if all of this sounds overwhelming — that’s because it is. But the right partner makes it manageable.
MailSPEC was built with multi-country compliance for enterprise messaging in mind. Here’s how we help:
And no matter where your people are — or how fast regulations evolve — MailSPEC keeps you one step ahead.
While tools like MailSPEC are indeed critical, technology alone is not enough. Enterprises must also create these smart internal policies to support enterprise communication compliance standards worldwide.
✔️ Audit Your Jurisdictional Footprint
Map out where your employees, data centers, and clients are located — and understand the legal obligations in each of those areas.
✔️ Define Local vs. Global Policies
Set base policies that apply globally (e.g., encryption), but allow for local add-ons (e.g., retention rules, language-specific consent notices).
✔️ Establish Approval Workflows
Then, for sensitive or regulated communications, create workflows that ensure legal or compliance teams can review messaging before it’s sent.
✔️ Train and Empower Your People
Give your employees clear guidelines too!— and the tools they need — to communicate securely and compliantly, without slowing down productivity.
✔️ Partner with a Trusted Compliance Platform
MailSPEC provides the foundation for global communication that’s both secure and adaptable to evolving regulatory landscapes.
Enterprise messaging does not happen in a vacuum. A message that’s perfectly compliant in one country could trigger fines in another. And that’s the reality of doing business in a global, digitally connected world.
Multi-jurisdictional compliance for enterprise messaging is not just a legal obligation — it’s a business necessity. And the more proactive and structured your approach, the less likely you are to fall behind.
So whether you are expanding into new markets or shoring up your existing compliance strategy, MailSPEC gives you the control and clarity you need — without the additional complexity for your teams.
Let’s talk about how MailSPEC can support your growth and protect your communications at every level.
MailSPEC、JACE Version 3 (Journaling, Archival, Compliance, and Escrow)を発表
主権に基づくクライアントサイドAIが、規制産業向けに比類なきコンプライアンス、データ主権、監査準備性を提供。
日本、2026年4月6日 – 安全性の高い企業間コミュニケーションおよびインテリジェントコンプライアンスプラットフォームのパイオニアであるMailSPECは、本日、世界で最も規制の厳しいセクター向けに独自設計されたコンプライアンス分類AIエンジン「JACE Version 3」の一般提供を開始したことを発表いたします。クライアント上(エンドツーエンド暗号化)で動作し、クラウドデータ転送ゼロ、多チャネル(メール、チャット、ビデオ、ファイル分類器)対応ソリューションとして構築されたJACEは、強固な規制コンプライアンスを達成しつつ、主権に基づく展開におけるプライバシー保護というジレンマを解決するものです。
JACE 3(Journaling, Archival, Compliance, and Escrow)は、新たなSDKを提供し、「JACE Policy Script」により駆動されるプログラミングインターフェースを搭載しております。これにより、コンプライアンス責任者およびCISOは、各ビジネスプロセスや規制要件ごとにポリシーを細かく調整することが可能となります。Office 365、Oracle NetSuite、SAP、財務アプリケーション、国家安全保障ソフトウェアとのシームレスな統合は他に類を見ず、さまざまな規制ポリシーや業界アプリケーションへの適応力において、本コンプライアンスプラットフォームを際立たせております。
JACE 3は、銀行、医療機関、政府機関、多国籍企業がAIを活用しつつ、最も価値ある資産である内部独自データおよびビジネスの「ノウハウ」の機密性を損なうことなく活用できる環境を提供いたします。内部コミュニケーションには、競争優位性および顧客データセットのプライバシーを支える組織の「秘伝のタレ」が含まれております。
規制監視の強化および地政学上のデータリスクが高まる時代において、JACE 3は、機密情報をクラウドや公開LLMに送信することを受け入れられない組織にとっての最も信頼できるソリューションであります。本プラットフォームは、すべてのAIタスクを完全に端末側または「クライアントサイド」で処理するため、取り込みから監査証跡に至るまで、エンドツーエンド暗号化と完全なデータ主権を保証いたします。
「内部コミュニケーション データは、組織の知的財産、顧客記録、取引戦略、患者履歴、戦略計画など、組織の王冠に輝く宝石であります」とMailSPEC研究開発部長 Tanguy Godquin PhDは述べています。「JACE 3は、単に当該データを保護するだけでなく、ポリシーベースのメタデータ索引により積極的に発見・分類・統治します。他のソリューションでは、企業グレードのAIコンプライアンスをゼロエクスフィルトレーションリスクで実現することはできません。」
JACE 3の主要イノベーション
本リリースの核心は、主権に基づくクライアントサイドAI統治エンジンであります。「クラウド依存型」コンプライアンスツールとは異なり、JACE 3は先進的なポリシーモデルを組織のインフラまたはエンドユーザー端末上で直接実行します。機密情報は決してクライアント環境外へ持ち出されません。このアーキテクチャにより、規制産業における最大のコンプライアンスリスクである、国外の管轄区域や第三者LLMへの意図せぬデータ転送を根本的に排除いたします。
JACE 3は強力なソフトウェア開発キット(SDK)を導入し、以下のミッションクリティカルシステムとの摩擦のない統合を実現します。
• 銀行トレーダーおよびコンプライアンス(KYC/AML)プラットフォーム(通信・取引記録・市場データのリアルタイム監視)
• SAPおよびOracle NetSuite ERP環境(財務ワークフロー全体での自動ポリシー適用)
• 主要医療記録システム(クラウド露出なしでの患者データおよび臨床ノートのコンプライアント分析)
開発者は、暗号化境界を完全に維持したセキュアAPIにより、既存ワークフローへJACEインテリジェンス検知およびポリシーベース統治を数日で埋め込むことが可能です。
JACE 3は、独自の検知アルゴリズムにより、メール、添付ファイル、チャットログ、ERPエントリ、ドキュメントリポジトリ内の独自データおよび規制対象データをリアルタイムで特定いたします。検知後、分類エンジンは組織固有のポリシーを適用し、自動的に以下の処理を実行します。
• 感度レベル、規制タグ、保管ルール、データ所有者などの豊富なメタデータによるコンテンツ索引
• すべてのAIインタラクションに対する不変の監査証跡生成
• eDiscovery、規制審査、内部調査向け記録の準備
• 「今保存して後で復号」脅威に対する静止時量子安全暗号化の提供
この機能により、コンプライアンスは「反応的な負担」から「能動的な戦略優位性」へと変貌します。金融機関はMiFID II、SOX、SEC規則17aおよび日本の規制要件への遵守をワンクリックレポートで証明可能となり、医療機関はHIPAA、GDPR、APPIおよび国内医療規制への適合を容易に達成しつつ、臨床研究ワークフローを加速させることができます。
主権に基づく統制の重要性が高まる背景
主権に基づくAIソリューションの需要はもはやニッチではなく、戦略的必然であります。地政学上の緊張、米国CLOUD Actなどの域外法、厳格な地域規制により、データローカライズ技術の採用が加速しております。Grokipediaの[1]「2026 in Information Technology」によると、組織はデータ主権およびプライベートAI展開を優先し、第三者インフラへの制御委譲を避ける動きを強めております。Deloitteは2026年単年で主権に基づくAIコンピュートへの世界投資額が約1,000億米ドルに達すると予測しております。
欧州連合では、EU AI Act[2](2026年8月完全施行)およびEU Data Act[3]により、デジタル主権が産業政策の要石となっております。違反時には世界売上高の最大7%の罰金が科され、Gaia-X[4]などの取り組みがEU中心の連合型インフラを推進しております。Gartnerの予測[5]によれば、2030年までに欧州・中東企業の75%以上が「geo repatriation戦略」を採用し、ワークロードを主権に基づくまたは地域クラウドへ移行すると見込まれております。
GCC地域も同様の動きを進めております。サウジアラビア、UAE、カタールでは、政府・医療・金融データのローカライゼーションを国家戦略で義務付けております。PwCの2026年経済見通し[6]では、データ主権がAI展開の鍵となり、規制当局は機密ワークロードに国内インフラを要求すると指摘されております。
日本は、個人情報保護法(APPI)[7]の下で技術的自立を着実に推進しております。欧州連合と日本のEU-Japan Digital Week[8]やEU-Japan Digital Partnership[9](2022年開始)は、データ主権およびFAIRデータ原則を信頼できる国境を超えたパートナーシップの基盤として位置づけております。
日本における主権に基づくクライアントサイドAIの緊急的必要性:国家安全保障および機密データ保護のための戦略的必須事項
日本にとって、MailSPECのJACE Version 3のような主権に基づくクライアントサイドAIソリューションの採用は、単なる技術的アップグレードではなく、国家安全保障、規制遵守、経済レジリエンスのための戦略的必然であります。2025年12月、内閣は新たな5か年サイバーセキュリティ戦略[10]を採択し、国家支援型サイバー攻撃を「深刻な安全保障上の脅威」と明示するとともに、能動的サイバー防御(ACD)を含む積極的防衛・抑止へと舵を切りました(国家サイバーセキュリティオフィス、内閣官房、サイバーセキュリティ戦略概要、2025年12月23日)[10]。これは2025年5月16日成立の画期的な能動的サイバー防御法[10]を直接的に踏まえたもので、2027年までに段階的完全施行が予定されており、警察・自衛隊による脅威の事前無力化、通信データの安全な利用、公私連携の強化、新たなサイバー協議会の設置、組織再編などを含みます(能動的サイバー防御法成立関連報告、2025年5-8月;Baker McKenzie分析、2026年1月22日)[10]。
同時に、日本は個人情報保護法(APPI)の強化を継続しております。2026年の改正見直しでは、個人の権利強化、執行力向上(行政制裁金の導入可能性)、越境データ移転ルールの精緻化、AIリスク対応が焦点となっており、域外露出およびサプライチェーン脆弱性への懸念に対応しつつ、責任あるデータ活用を促進しております(個人情報保護委員会、APPI三年に一度の見直し方針、2026年1月9日)[11]。
日本の最も価値ある資産である金融取引データ、医療記録、知的財産、政府機密は、外国からの召喚状、地政学上の強制、産業スパイ活動から守るため、絶対的な日本統制下に置かれなければなりません。クラウドベースAIは機密情報を外部システムへアップロードする必要があり、許容し難いエクスフィルトレーション経路を生み出します。JACEの端末側または完全クライアントサイドアーキテクチャはこのリスクを排除します。組織境界外へ機密データが一切流出せず、エンドツーエンド暗号化およびポリシーベースメタデータ索引により、独自コンテンツの自動検知、保管・監査ルールの適用、不変の監査証跡生成を実現します。JACE 3はAPPIおよび新たなサイバーセキュリティ要件に完全に適合しております。
この必要性は、富士通が2026年2月に発表した「Made in Japan」主権に基づくAIサーバーの鹿島工場での製造開始(2026年3月稼働、最新プロセッサおよび機密計算機能搭載)[12]など、産業界の動きからも明らかであります。銀行、医療、国家防衛などの規制セクターでは、クライアントサイドAIのみが強力なインテリジェンスを主権を譲渡することなく提供可能です。日本がAI駆動型サイバーリスクおよび国家レベルの脅威の中で技術的自立を加速させる中、JACEは国家のデータ王冠に輝く宝石を守りつつ、責任あるAIイノベーションを可能にするセキュアかつ監査可能な基盤を提供いたします。これはまさに日本のサイバーセキュリティ・データ保護・経済安全保障枠組みが求めるバランスであります。
クライアントサイドAIおよびエンドツーエンド暗号化が最優先される理由
規制産業、政府機関、国家安全保障分野において、クライアント上で真のエンドツーエンド暗号化を伴うAI処理は選択肢ではなく、唯一責任あるアーキテクチャであります。クラウドベースAIは、召喚状、侵害、インサイダー脅威を通じてデータエクスフィルトレーションのベクターを生み出します。クライアントサイド処理は、平文データを組織のセキュリティ境界内に常時留め置きます。
エンドツーエンド暗号化により、AIモデル自体がコンテンツを開示するよう強制されることもありません。この手法は、先進的分析で指摘される「主権危機」に直接対応します。集中型クラウドアーキテクチャは組織が最も機密性の高い資産の制御を放棄せざるを得なくします。これに対し、JACE 3は絶対的な機密性を維持しつつ強力なインテリジェンスを提供いたします。これは機密情報を扱う国家安全保障機関、患者プライバシーを守る医療提供者、顧客および競争データを保護する金融機関にとって極めて重要です。
業界専門家も一致しております。Grokipedia[13]が示すように、2026年にはプライベートAI展開およびデータ主権の重要性が一層高まっており、公開クラウド依存および規制要件に伴うリスクを軽減するために不可欠となっております。クライアントサイド暗号化、機密計算、顧客管理キー は、高セキュリティおよび規制産業における標準要件となっております。
実績と提供状況
JACE 3の早期導入企業からは以下の劇的な成果が報告されております。
• コンプライアンスeDiscovery時間の94%削減
• パイロット展開におけるデータ転送インシデントゼロ
• 規制審査向け完全監査準備完了
• JACE Policy ScriptによるAIおよび分類のチューニング
• SDKによるKYC/AMLプラットフォームへのシームレス統合
JACE Version 3は、オン-premise、エアギャップ、ハイブリッド主権展開向けに即時提供可能です。SDKは主要プログラミング言語をサポートし、包括的なドキュメント、リファレンス実装、エンタープライズサポートパッケージを同梱しております。
MailSPECについて
MailSPECは、コミュニケーションチャネル向けAI統治およびコンプライアンス技術を提供し、世界で最もセキュリティ意識の高い規制組織から信頼を得ております。主権、データプライバシー、規制卓越性への揺るぎない取り組みにより、MailSPECは企業および公共サービス機関が、ますます複雑化する規制環境において自信を持ってイノベーションを推進できる環境を整えます。
詳細は www.mailspec.com をご覧ください。
メディアお問い合わせ先
Director of Investor relations and public communications, MailSPEC
+81-46-872-4950 又は japan@mailspec.com
引用文献(Wordで各URLをハイパーリンクに設定し、番号をブックマークとしてご利用ください)
1. Grokipedia. (2026). 2026 in Information Technology. Retrieved March 14, 2026, from https://grokipedia.com/page/2026_in_information_technology Deloitte. (2025). Technology, Media & Telecommunications Predictions 2026: A new era of self-reliance – Navigating technology sovereignty. Deloitte Insights. https://www.deloitte.com/us/en/insights/industry/technology/technology-media-and-telecom-predictions/2026/tech-sovereignty.html Deloitte Global. (2025). Deloitte 2026 Technology, Media & Telecommunications Predictions. Press release, November 2025. https://www.deloitte.com/global/en/about/press-room/2026-tmt-predictions.html
2. EU AI Act text (eur-lex.europa.eu), Article 99.
3. (2023). Regulation (EU) 2023/2854 of the European Parliament and of the Council of 13 December 2023 on harmonised rules on fair access to and use of data (Data Act). Official Journal of the European Union. https://eur-lex.europa.eu/eli/reg/2023/2854/oj
4. Gaia-X European Association for Data and Cloud AISBL. (n.d.). Gaia-X: A Federated Secure Data Infrastructure. Official website. https://gaia-x.eu/
5. Gartner, Inc. (2025, November 12). Gartner Survey Reveals Geopolitics Will Drive 61% of CIOs and IT Leaders in Western Europe to Increase Reliance on Local Cloud Providers. Press release. https://www.gartner.com/en/newsroom/press-releases/2025-11-12-gartner-survey-reveals-geopolitics-will-drive-61-percent-of-cios-and-information-technology-leaders-in-western-europe-to-increase-reliance-on-local-cloud-providers
6. PwC. (2026, January 6). Five GCC economic themes to watch in 2026. PwC Middle East. https://www.pwc.com/m1/en/blog/five-economic-themes-to-watch-2026-gcc.html
7. https://www.japaneselawtranslation.go.jp/en/laws/view/4241/en
8. EURAXESS (European Commission). EU-Japan Digital Week events listing: https://euraxess.ec.europa.eu/worldwide/japan/events/eu-japan-digital-week-2025 (for the 2025 edition, with similar framing).
9. Factsheet on the Japan-EU Digital Partnership (from the launch in 2022): https://digital-strategy.ec.europa.eu/en/library/japan-eu-digital-partnership-factsheetJoint Statement of the Third Meeting of the EU-Japan Digital Partnership Council (May 12, 2025): https://digital-strategy.ec.europa.eu/en/library/joint-statement-third-meeting-european-union-japan-digital-partnership-council
10. National Cybersecurity Office (NCO), Cabinet Secretariat, Japan. (2025, December 23). Outline of the Cybersecurity Strategy (Tentative English translation). https://www.cyber.go.jp/pdf/policy/kihon-s/cs_strategy2025_abstract_english.pdf Cabinet Secretariat, Japan. (2025, December 23). サイバーセキュリティ戦略 [Cybersecurity Strategy]. https://www.cyber.go.jp/pdf/policy/kihon-s/cs_strategy2025.pdf House of Representatives, National Diet of Japan. (2025). Bill on the Development of Active Cyber Defense (Enacted May 16, 2025). https://www.shugiin.go.jp/internet/itdb_gian.nsf/html/gian/honbun/houan/g21306007.htm Cabinet Secretariat, Japan. (2025). サイバー安全保障に関する取組(能動的サイバー防御の実現に向けた検討など). https://www.cas.go.jp/jp/seisaku/cyber_anzen_hosyo_torikumi/index.html Baker McKenzie – Connect On Tech. (2026, January 22). Japan’s New Active Cyber Defense Law: Impact on Businesses. https://connectontech.bakermckenzie.com/japans-new-active-cyber-defense-law-impact-on-businesses
11. Personal Information Protection Commission (PPC), Japan. (2026, January 9). System Reform Policy under the Triennial Review of the Act on the Protection of Personal Information Has Been Decided (January 9, 2026). https://www.ppc.go.jp/en/topix/triennial_review_2026_02/
12. Fujitsu Limited. (2026, February 12). Fujitsu Group starts manufacturing sovereign AI servers in Japan to enhance digital sovereignty. Fujitsu Global. https://global.fujitsu/en-global/pr/news/2026/02/12-01
13. Grokipedia. (2026). 2026 in Information Technology. Retrieved [current date, e.g., March 14, 2026], from https://grokipedia.com/page/2026_in_information_technology